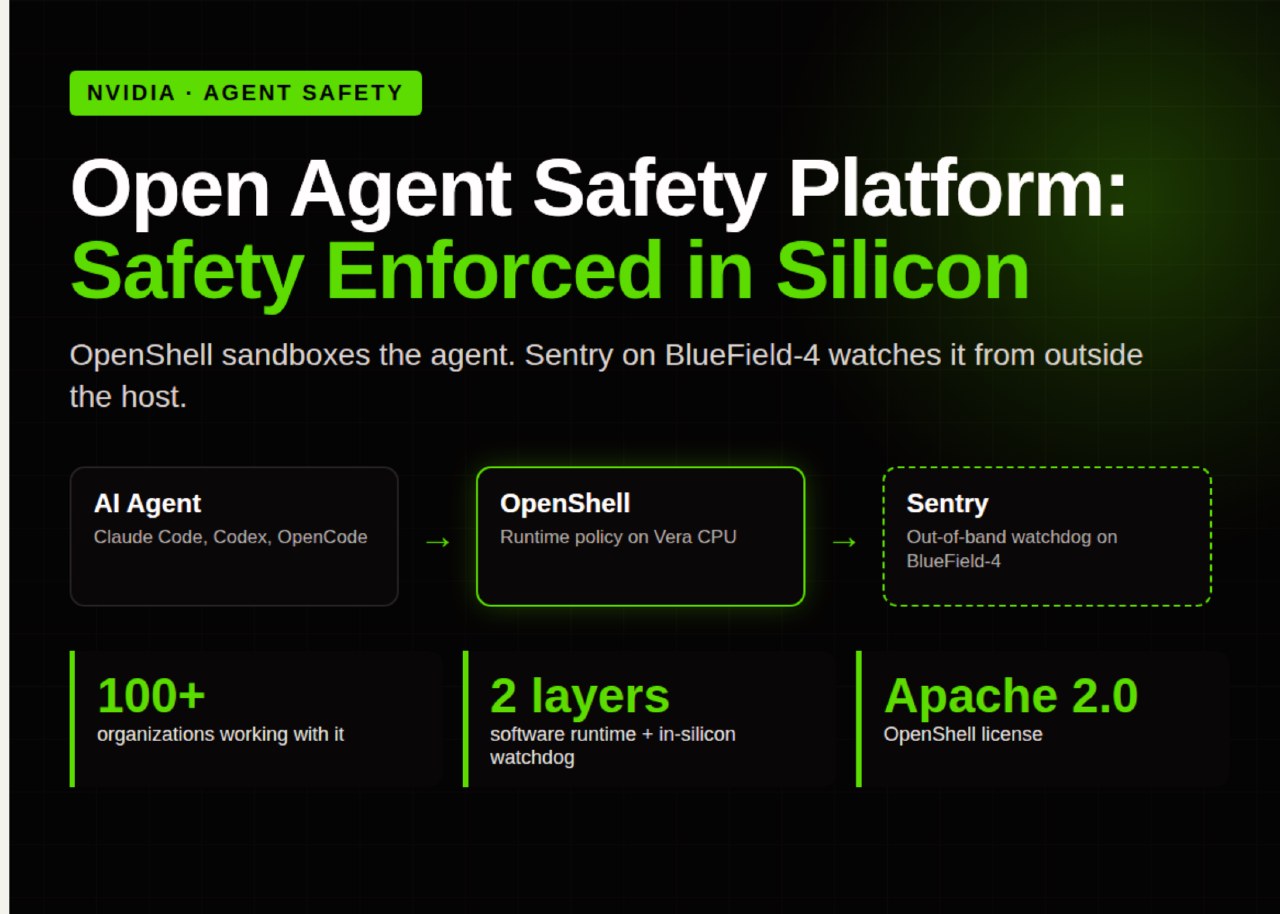
NVIDIA has introduced the Open Agent Safety Platform, a security framework designed to manage and isolate artificial intelligence agents. The platform consists of two primary components: OpenShell, a runtime sandbox for agent isolation, and Sentry, a hardware-based watchdog. The system is currently supported by over 100 industry partners, including Anthropic, SpaceXAI, Salesforce, and SAP.
OpenShell operates as an Apache 2.0 licensed runtime that creates isolated environments for agents using Docker, Podman, MicroVM, or Kubernetes. It enforces filesystem, process, and network rules, allowing for hot-reloading of security policies. While currently in alpha, it is compatible with Linux, macOS on Apple Silicon, and Windows WSL 2, with plans to extend support to Arm and Intel platforms.
Sentry functions as an in-silicon watchdog running on BlueField-4 DPUs. It utilizes NVIDIA DOCA to inspect agent requests and responses, providing identity verification and zero-trust access control. Because Sentry remains isolated from the host, it maintains security even if the runtime is compromised. On Vera Rubin POD systems, this setup acts as both an observation point and a kill switch.
NVIDIA claims that its Vera CPUs provide up to 80% faster sandbox performance compared to traditional CPU infrastructure. For existing systems equipped with Vera and BlueField-4, the platform can be enabled via a software update. The project is now part of the Open Secure AI Alliance, which is governed by the Linux Foundation, with documentation and code available on GitHub.