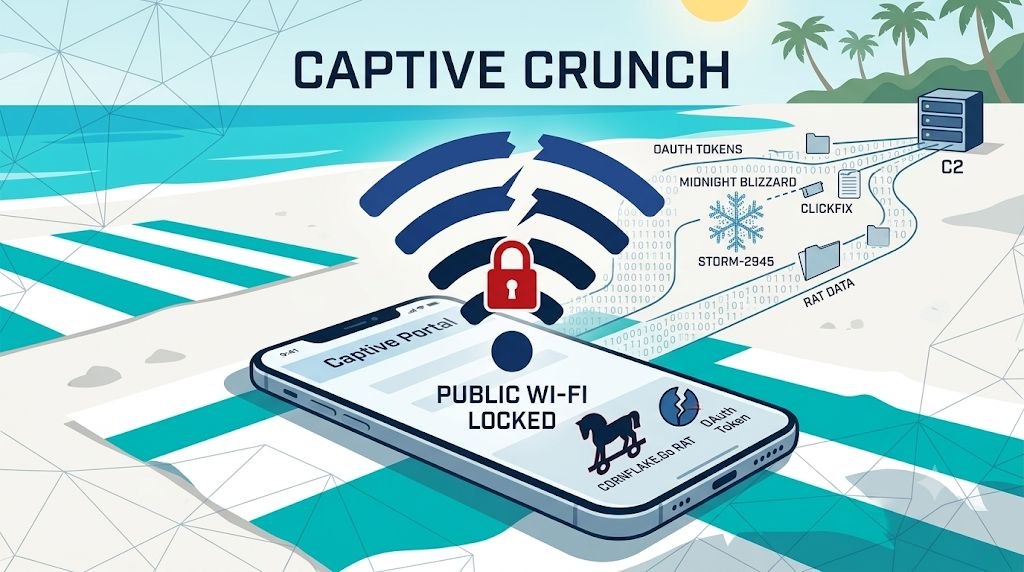
In the spring of 2026, cybersecurity experts identified a new spoofing campaign dubbed CaptiveCrunch. The operation is attributed to the APT group Storm-2945, which functions as a subgroup of Midnight Blizzard.
Microsoft Threat Intelligence released a technical analysis of the campaign in July 2026. The attack vector involves compromising captive portals within public Wi-Fi networks at hotels worldwide to target business travelers.
The attackers employ device-code phishing and the ClickFix technique to distribute RAT malware. These malicious files are disguised as legitimate system updates, bypassing traditional security perimeters.