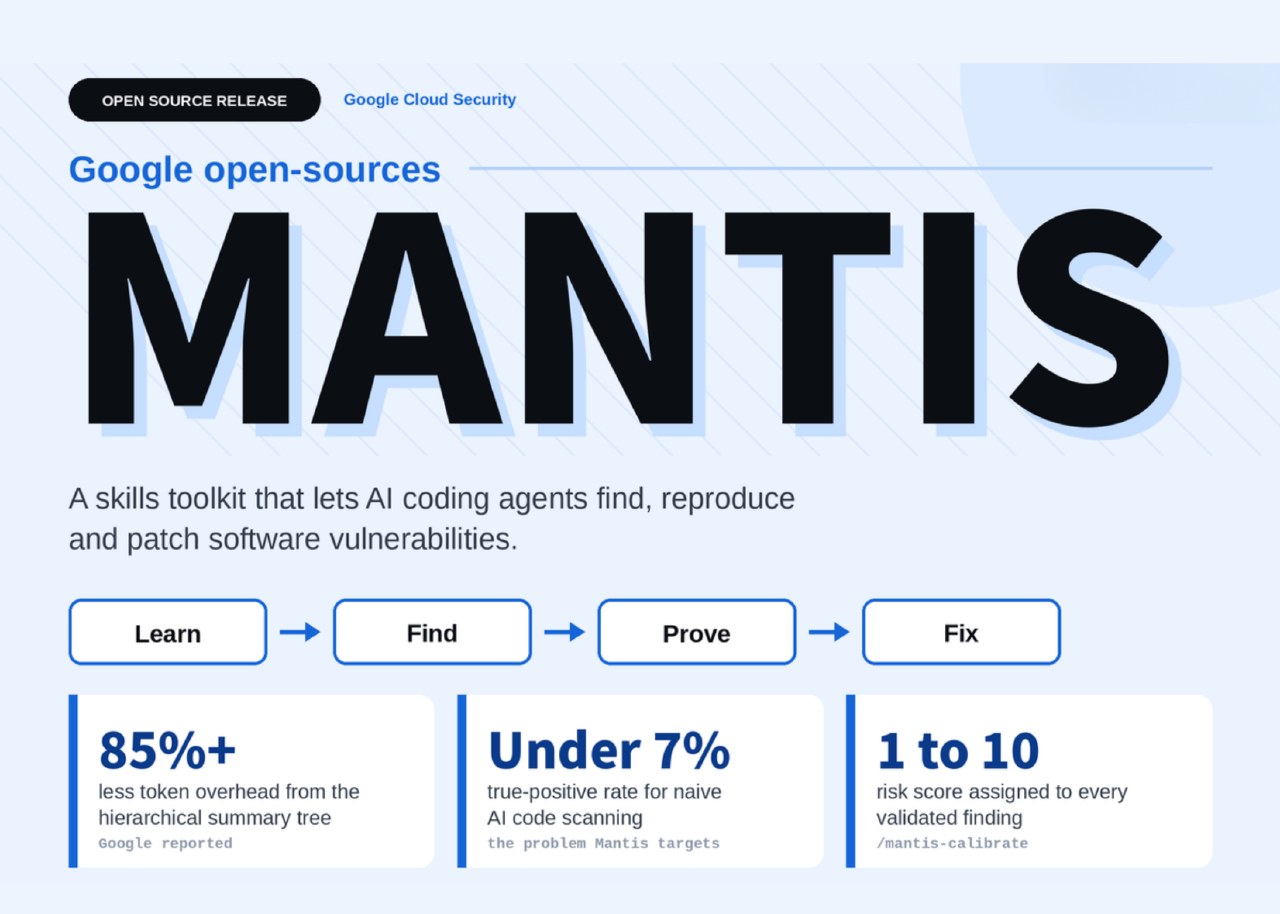
Google has released Mantis, an open-source modular toolkit designed to assist coding agents in identifying, reproducing, and patching software vulnerabilities. Unlike automated scanners, Mantis functions as a set of slash commands integrated into existing agent frameworks, requiring defined execution rules.
The toolkit operates through sequential stages managed by a supervisor skill, mantis-meta-agent. Initial phases involve analyzing version control history, mapping directories, and building architectural knowledge bases. Subsequent stages filter findings, remove duplicates, and apply negative rules to exclude non-relevant issues.
The final stages focus on proving and fixing vulnerabilities. Mantis executes payloads within isolated environments like gVisor or virtual machines with disabled networking. The system then assembles exploit chains, applies patches, verifies fixes, and assigns risk scores on a scale of 1 to 10.
A specific skill, mantis-advise, allows developers to query threat models and past bug patterns before writing new code to prevent recurring issues. The toolkit is currently available for local and internal evaluation, supporting frameworks such as Gemini CLI, Antigravity CLI, and the Google ADK.