

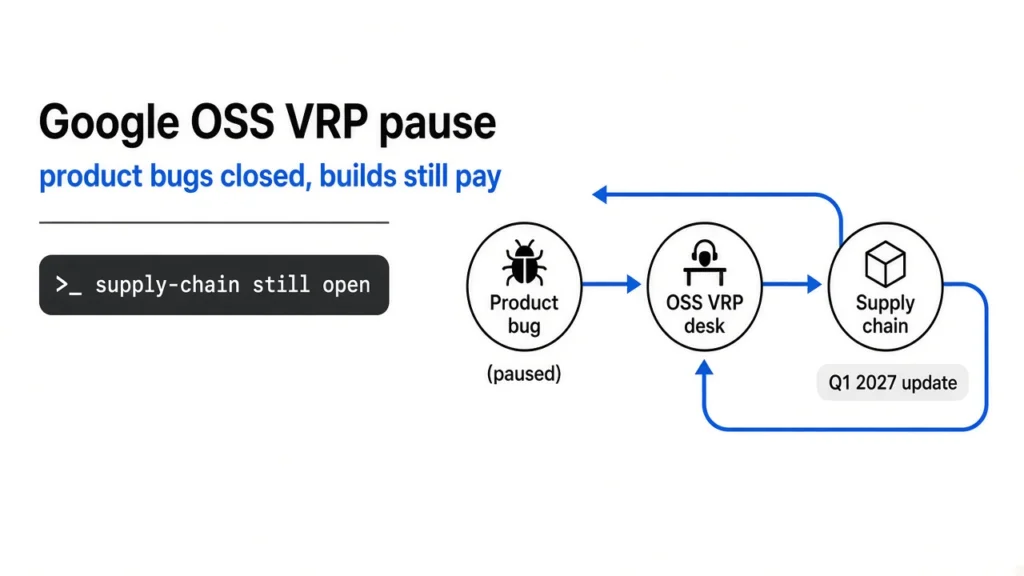
Google has officially suspended the product vulnerability submission channel within its Open Source Software Vulnerability Reward Program (OSS VRP). The decision, effective from October 1, follows a surge in low-quality reports generated by artificial intelligence, which have overwhelmed the company's security engineers and open-source maintainers.
The company stated that the influx of AI-generated reports includes numerous false positives and hallucinations that require manual verification. This process consumes significant resources, distracting teams from addressing genuine security threats. Google plans to provide an update on the program's status in the first quarter of 2027 after revising its submission and review mechanisms.
The suspension applies specifically to product vulnerability submissions. Reports submitted before October 1 remain unaffected, and the program will continue to accept submissions related to supply chain security. Additionally, vulnerabilities affecting Google Cloud products may still be reported through the separate Cloud VRP channel.
This trend of automated, low-quality submissions is becoming a broader issue within the cybersecurity industry. Similar challenges have been reported by the Linux community, where maintainers have struggled with an increasing volume of non-existent vulnerabilities generated by automated tools, forcing changes to their internal workflows.
