Google Raises Payouts for Chrome Security Vulnerabilities
Google has increased the base reward for memory corruption vulnerabilities in Chrome to $2000, with top payouts for critical flaws reaching $20 000.

Google has increased the base reward for memory corruption vulnerabilities in Chrome to $2000, with top payouts for critical flaws reaching $20 000.

Google has revised its Chrome bug bounty program, increasing payouts for memory corruption and write vulnerabilities up to $20,000 and introducing new rewards for fuzzing tools.

Security firm XBOW earned a $250 000 bounty from Google after using an AI model to discover and chain three Chrome vulnerabilities in just six days.

Google has increased payouts for its Chrome bug bounty program, offering up to $20 000 for critical vulnerabilities and introducing new rewards for testing tools.

A critical arithmetic bug in the XRP Ledger could have allowed for unauthorized token creation, prompting an emergency patch in September 2026.

The use of AI tools has doubled the number of vulnerability reports on the Standoff Bug Bounty platform, yet verified findings increased by only 48% due to a surge in low-quality submissions.

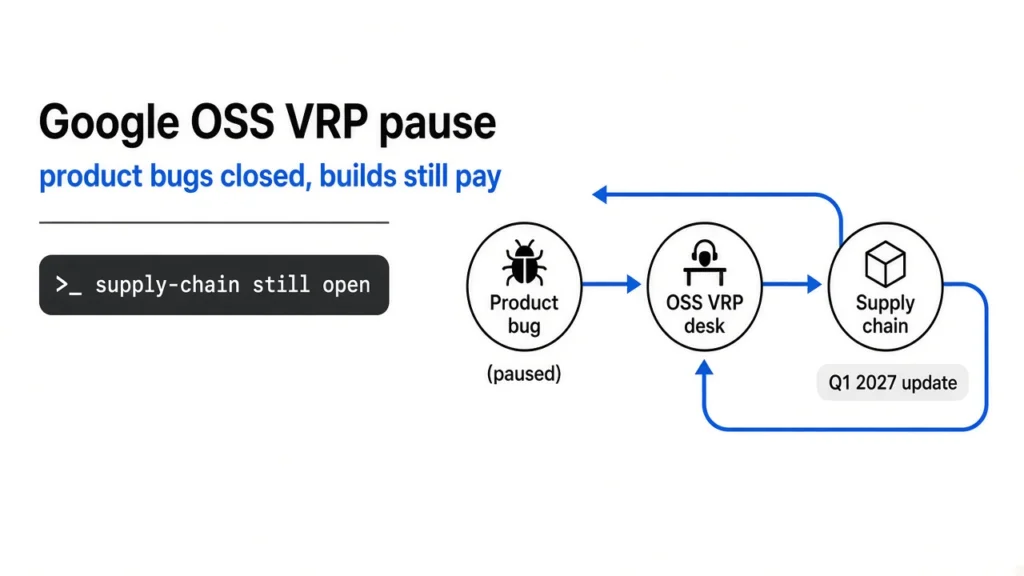
Google has halted new submissions to its open-source bug bounty program due to a surge of low-quality, AI-generated reports.

Google has paused its open source bug bounty program until 2027 following a surge in invalid, AI-generated vulnerability reports.

Google is shutting down its open-source vulnerability reward program for product reports by October 2026 due to an influx of AI-generated false reports.
Google has paused its open-source vulnerability reward program for product bugs due to an overwhelming volume of low-quality, AI-generated reports.

Google has paused its open-source bug bounty program for product vulnerabilities due to an influx of invalid, AI-generated reports.

Corporate spending on practical cybersecurity testing, including pentests and bug bounty programs, surged by 85% in the first eight months of 2026.
A 16-year-old researcher received a $5,000 bounty from Microsoft after using an AI bot to uncover a vulnerability exposing over 17 trillion records.

A teenager received a $5 000 bug bounty from Microsoft after using an AI bot to access a database containing 17 trillion records and 25 000 user accounts.

Intel has discontinued its long-standing bug bounty program, which offered rewards of up to $100,000 for identifying critical security vulnerabilities.

Intel has suspended its bug bounty program, which previously paid up to $100,000 per flaw, and shifted to a new disclosure platform that offers no financial rewards.

Security researchers used Anthropic’s Claude to breach OpenAI systems, earning a $6,500 bounty after gaining access to private source code.

Security researchers from Hacktron AI received a $6 500 bounty from OpenAI after using Anthropic’s Claude to identify and report a critical vulnerability in the company's internal systems.

Intel has discontinued its paid bug bounty program, replacing it with a non-monetary responsible disclosure initiative on the Intigriti platform.

Security researchers exploited vulnerabilities in OpenAI's systems using AI-generated code to gain access to internal repositories and employee accounts.