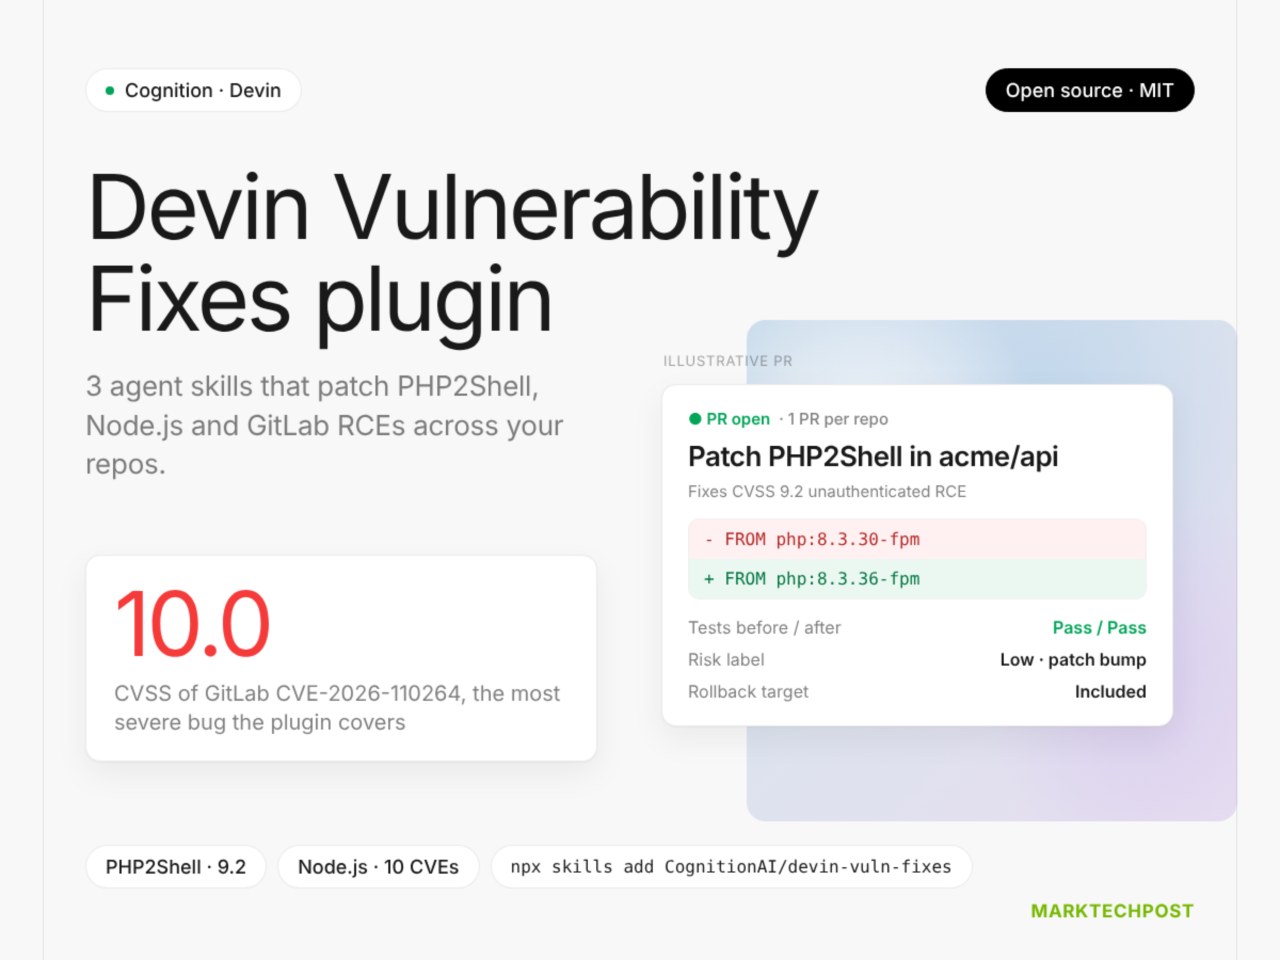
Cognition has released the Devin Vulnerability Fixes plugin, a set of three agent skills designed to identify and patch security flaws in PHP, Node.js, and self-managed GitLab environments. The tool is available as free, open-source software under the MIT license on GitHub.
The plugin addresses specific critical vulnerabilities, including the PHP2Shell flaws (CVE-2026-109618 and CVE-2026-109619) with a CVSS score of 9.2, and a GitLab integer overflow (CVE-2026-110264) rated at CVSS 10.0. It also covers 10 vulnerabilities in the October 2026 Node.js release, four of which are classified as high severity.
Unlike dependency-focused tools, this plugin targets the runtime layer, including base images, OS packages, and infrastructure-as-code. It accounts for specific patching challenges, such as version backporting in Debian and Ubuntu, where standard version checks may be misleading.
Users can install the plugin via the Devin Marketplace, the Devin CLI, or by using the npx command for other agents. Claude Code users can also integrate the tool through the marketplace. Once installed, the plugin can be triggered via natural language requests or specific slash commands for each platform.