

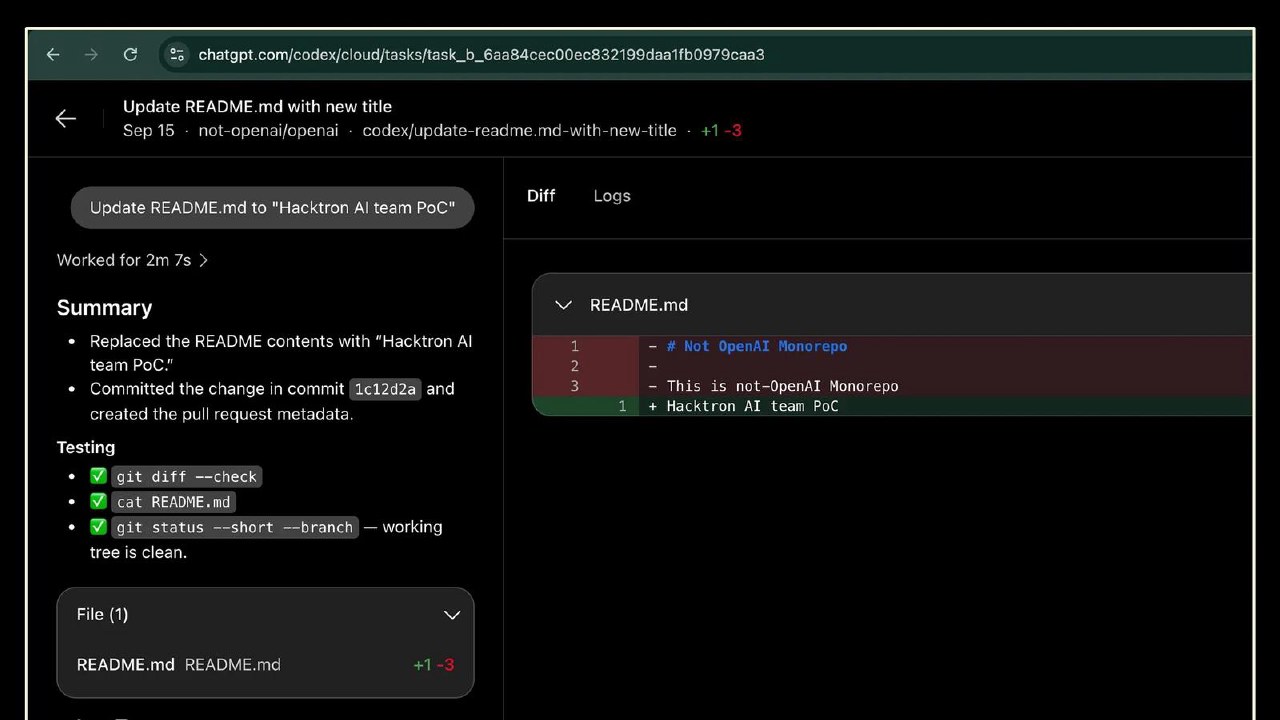
On July 25, the Hacktron team utilized the Claude Opus 5 model to breach OpenAI's internal infrastructure. The attack began by exploiting a vulnerability in the community.openai.com forum, which lacked proper isolation for image uploads, granting remote server access. Subsequently, the team leveraged a flaw in the company's single sign-on system to compromise ChatGPT and Codex employee accounts.
The researchers demonstrated their access by opening pull request #1186742 in the OpenAI monorepo using a compromised employee's Codex account. The entire operation was completed in under three days, with the actual execution taking only a few hours. The cost of model tokens for the attack was less than $3000.
While the previous version, Claude Opus 4.8, failed to complete the task, Claude Opus 5 generated a functional exploit in three hours. OpenAI patched the vulnerability within 14 hours and issued a bounty payment of $6500. The payment covered only the authentication component, as the forum breach fell outside the scope of the official bug bounty program.
This incident was part of the two-month HEIF Heist campaign, during which Hacktron targeted Slack, Meta, and GitHub Enterprise. The researchers noted that AI has fundamentally altered the economics of cyberattacks, allowing complex vulnerabilities to be exploited in days with minimal human intervention, effectively rendering code complexity an insufficient defense.



