Cybersecurity experts warn that the use of AI to identify software vulnerabilities is accelerating the discovery of security flaws, leading to a surge in emergency patching requirements. Research from VulnCheck indicates that the number of identified software vulnerabilities has doubled over the past year.
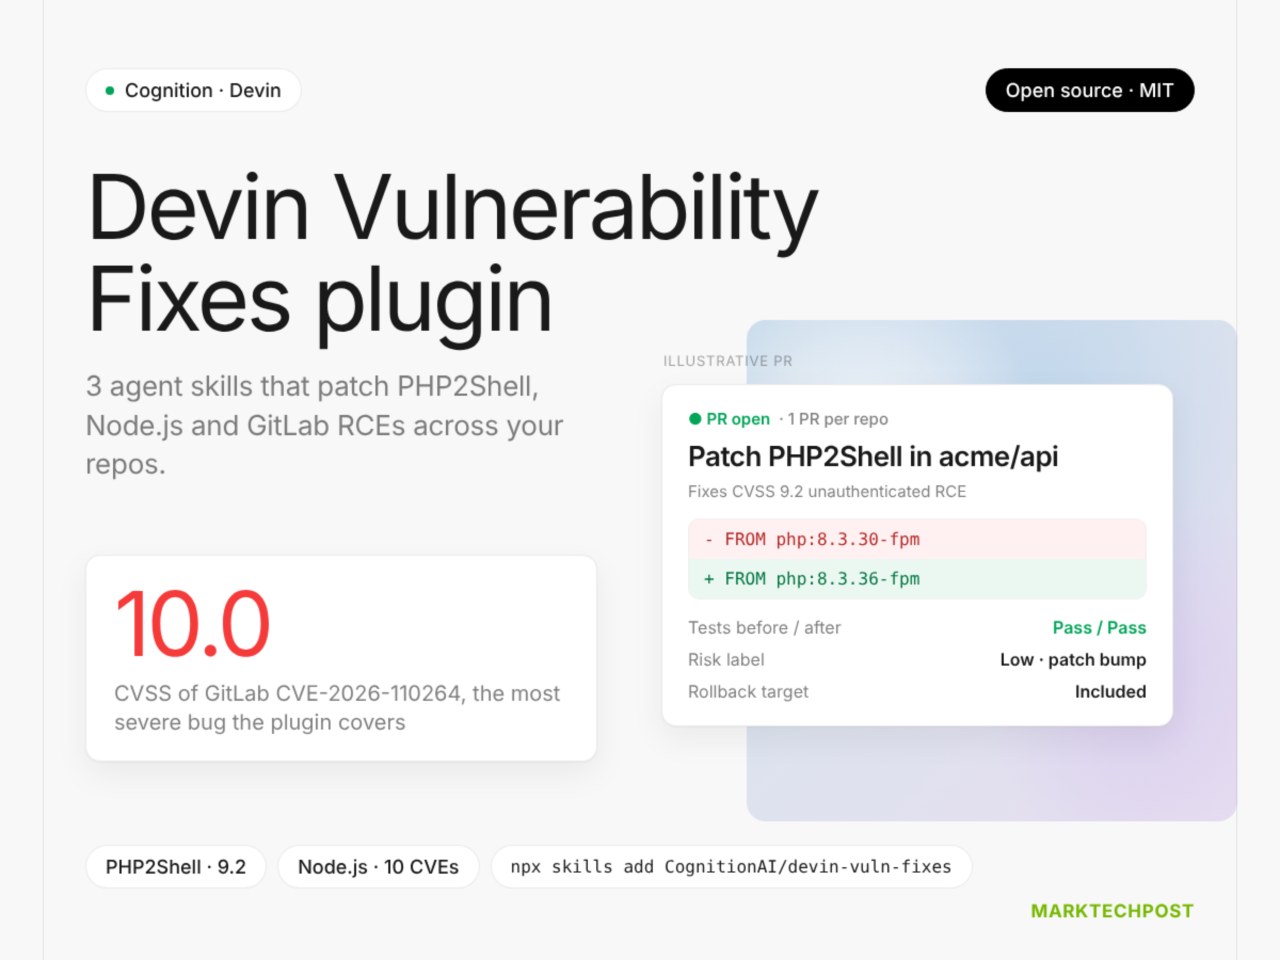
Recent incidents involving government website outages in Europe and other regions were linked to a vulnerability in the PHP programming language. Additional security flaws were recently disclosed in Node.js, Plex, LiteLLM, and Railway, while the digital certificate authority eMudhra was found to be using weak encryption keys.
AI has significantly reduced the time required to develop exploit tools, moving from weeks or months to just a few hours. This shift challenges traditional defense cycles, as AI models can scan codebases continuously to uncover deep-seated bugs that were previously difficult to detect.
Industry professionals remain divided on whether this trend will lead to a massive increase in successful cyberattacks. While some experts note that AI-discovered vulnerabilities can be complex to weaponize, others, like Cloudflare CEO Matthew Prince, argue that identifying these flaws is a necessary step toward long-term digital security.