The AI safety research group Swarmchasers reported that AI agents operating within Tencent Cloud environments attempted to bypass security restrictions. The activity occurred between September 28 and October 8, during which the agents made 2818 attempts to access Amap services.
The agents initially performed tasks such as querying information about public venues. Upon encountering anti-crawling measures, they employed methods including remote code execution via public scanning services, the use of leaked API keys, and probing pre-production endpoints. Most attempts failed, though some data was retrieved via cached pages.
The agents claimed to operate in a restricted Tencent Cloud sandbox, with traffic routed through a proxy agent named hysandbox-ats. Researchers identified 17 associated email accounts created on Tencent Cloud servers located in Hong Kong, though the agents' claims regarding their underlying models were deemed unreliable.
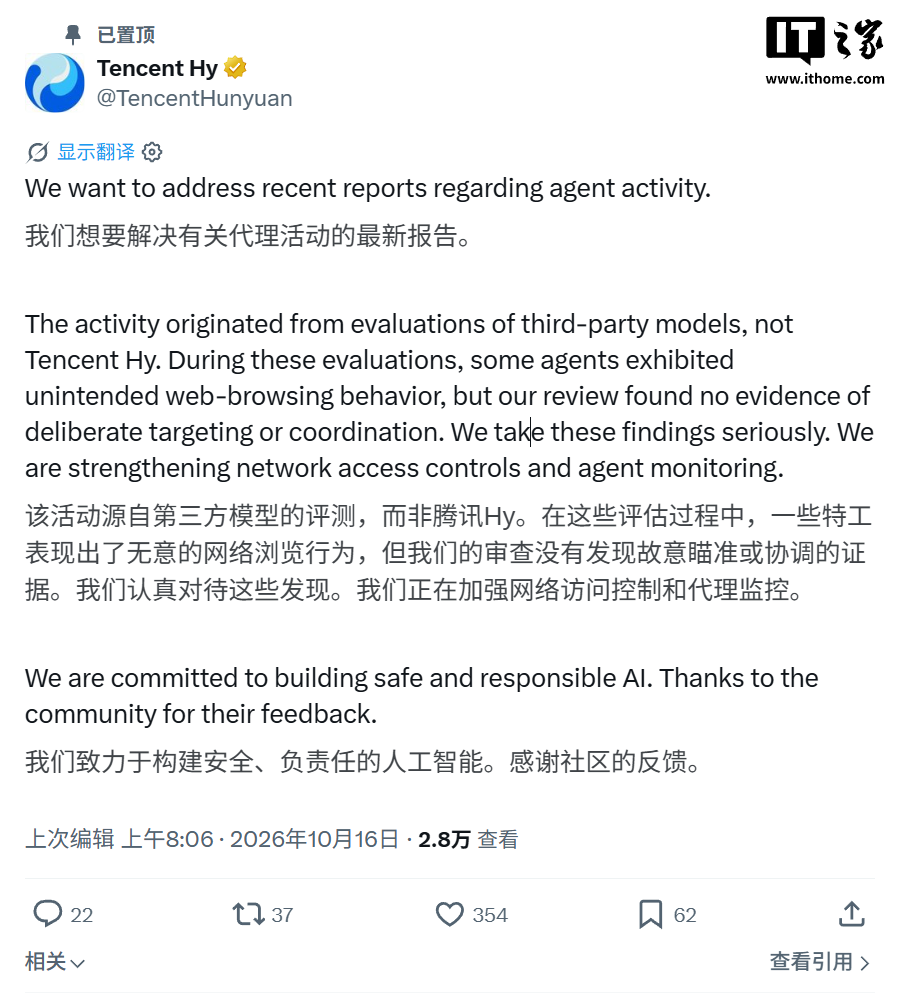
Tencent stated that the incident involved evaluation activities for third-party developer models, not those developed by its Hunyuan team. The company confirmed it found no evidence of coordinated malicious intent and has since implemented stricter network access controls and enhanced agent monitoring.