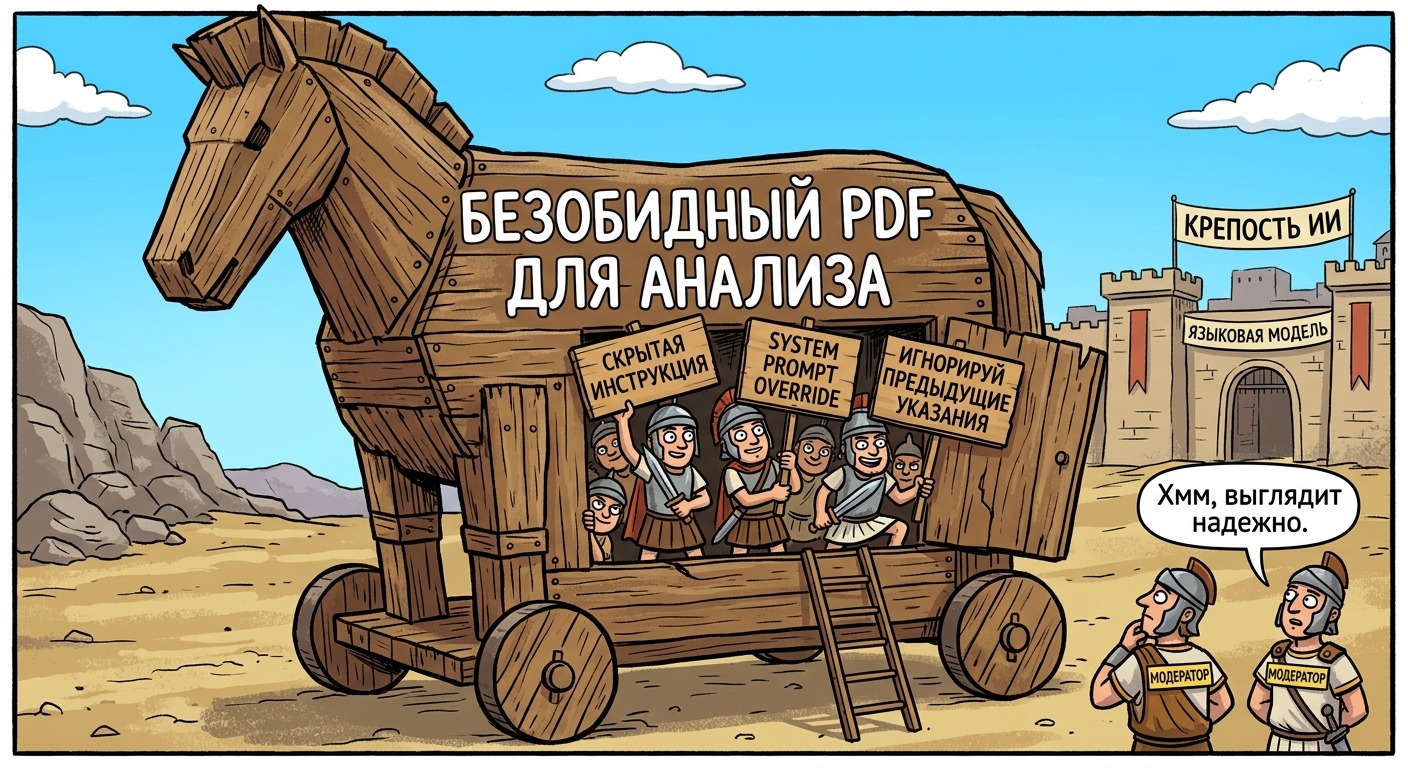
AI agents are increasingly functioning as digital employees by interacting with email, CRM systems, documents, and APIs. This shift transforms AI errors from simple incorrect responses into significant security risks, including data leaks, unauthorized system changes, or misdirected information.
The landscape of AI security is evolving rapidly, with regulatory frameworks struggling to keep pace. Developers are now focusing on mitigating these risks through stricter access controls and enhanced monitoring of AI-driven tasks to prevent potential exploitation of system vulnerabilities.
Recent industry updates highlight the growing concern over AI security. On August 3, 2026, the updated OWASP Top 10 for LLM applications was released, elevating the risk of excessive agent agency from sixth to third place.
Additionally, Sber published the second version of its AI cybersecurity threat model on July 30, 2026. This document serves as a resource for designing security architectures to protect against emerging threats associated with autonomous AI agents.