The PHP Foundation has disclosed a new remote code execution vulnerability, identified as CVE-2026-115560. The organization announced on October 24 that it will not release an immediate patch for the issue, as the vulnerability requires a specific combination of application configuration and code to be triggered.
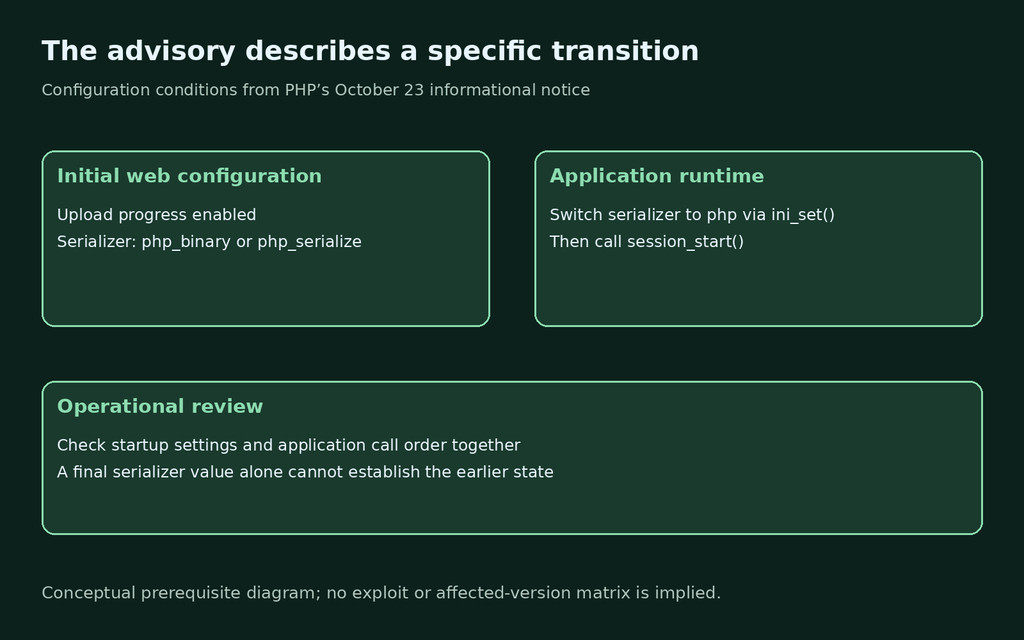
The flaw occurs only when the session.serialize_handler is set to php_binary or php_serialize, followed by a runtime switch to php using ini_set() and a subsequent call to session_start(). Additionally, the session.upload_progress.enabled setting must be active for the exploit to function.
The foundation considers this specific configuration rare in real-world applications. Unlike the previously addressed PHP2Shell vulnerability, this issue is currently managed through mitigation advice rather than a software update, though a permanent fix is planned for a future release.
Developers are advised to disable the upload progress feature by setting session.upload_progress.enabled to 0. This measure should remain in place until the foundation releases a version containing a formal security patch. Environments where this feature is already disabled require no further action.