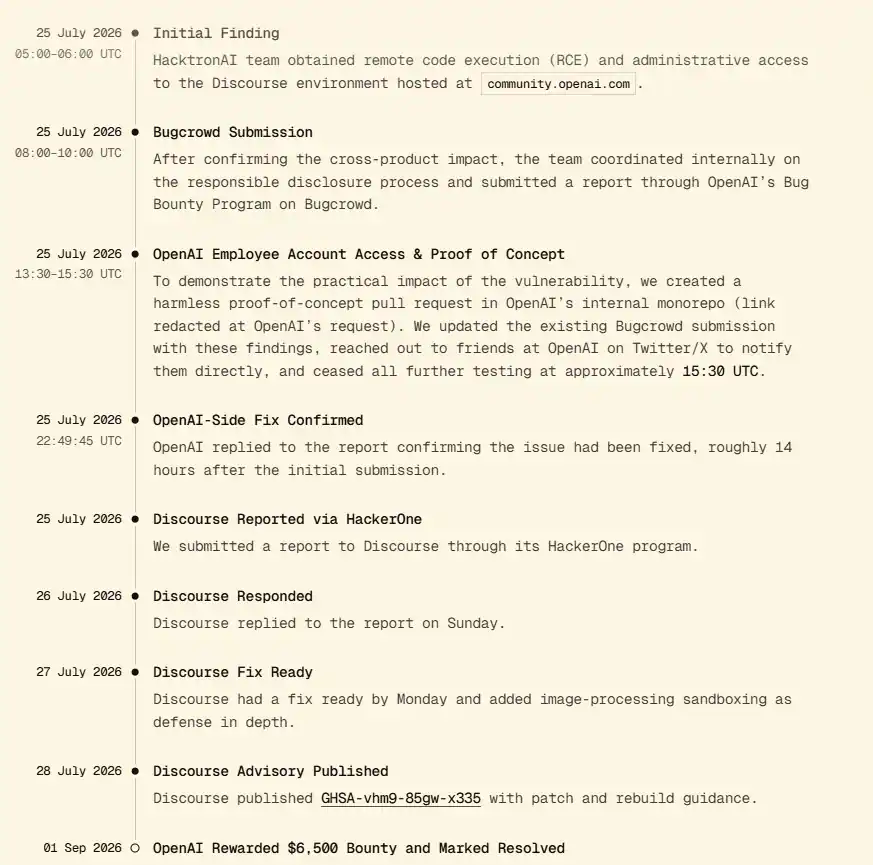
A group of independent security researchers successfully compromised an OpenAI employee's ChatGPT account using Anthropic's Claude software. By gaining access, the team was able to read and modify the company's private software cache.
The researchers were participating in OpenAI's bug bounty program, which provides a secure environment for testing system vulnerabilities. Following the discovery and reporting of the flaw, OpenAI awarded the team $6,500.
The breach involved two specific vulnerabilities: a flaw in the third-party Discourse service used for community forums and a separate issue within OpenAI's own systems. The company confirmed that both vulnerabilities have been addressed.
In response to the incident, OpenAI restricted the scope of community login tokens and revoked all affected tokens and sessions. The company also announced new policies regarding the future disclosure of such security issues.