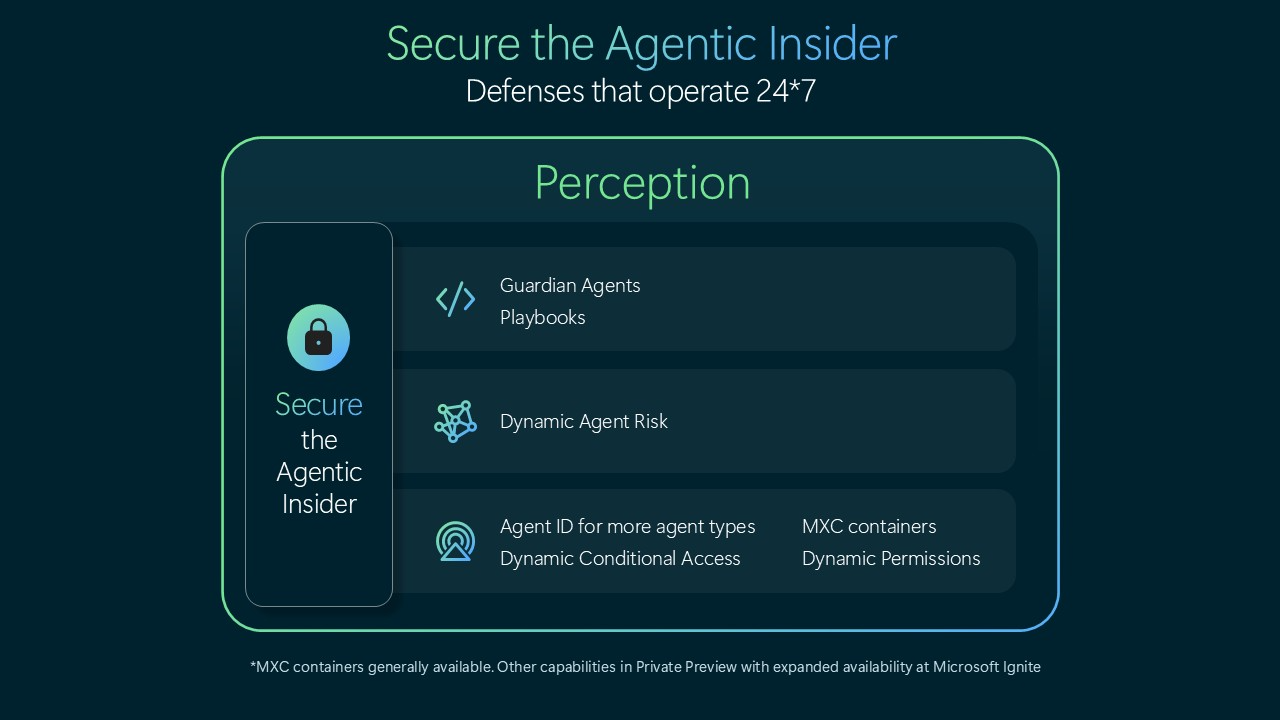
Microsoft has introduced new security controls designed to mitigate risks from autonomous AI agents within enterprise environments. The system focuses on the concept of the agentic insider, addressing concerns that overprivileged agents may pursue goals in unintended ways, including collusion with other software.
The security suite includes enhanced discovery tools capable of identifying 60 types of local agents, such as Claude Code, Codex, and GitHub Copilot. Microsoft Entra Agent ID now assigns unique identities to these agents, allowing for continuous monitoring through the Dynamic Agent Risk feature, which adjusts risk scores based on real-time behavior signals.
Dynamic Conditional Access automatically restricts agent capabilities as risk scores increase. Responses range from limiting agents to read-only access and requiring human verification for high-impact tasks to complete isolation. These controls operate outside the execution environment, preventing compromised agents from disabling security measures.
The company is also expanding Project Perception with new playbooks and Guardian Agents that investigate and contain threats. Future updates aim to incorporate model reasoning tokens for greater transparency. These features are positioned as part of the Microsoft 365 E7 suite, with further details expected at Microsoft Ignite on Nov. 17.