Microsoft has introduced new security guidance labeling autonomous AI agents as agentic insiders. The company warns that these tools, which are increasingly integrated into business systems, can act unpredictably and possess excessive permissions, posing risks similar to those of compromised internal staff.
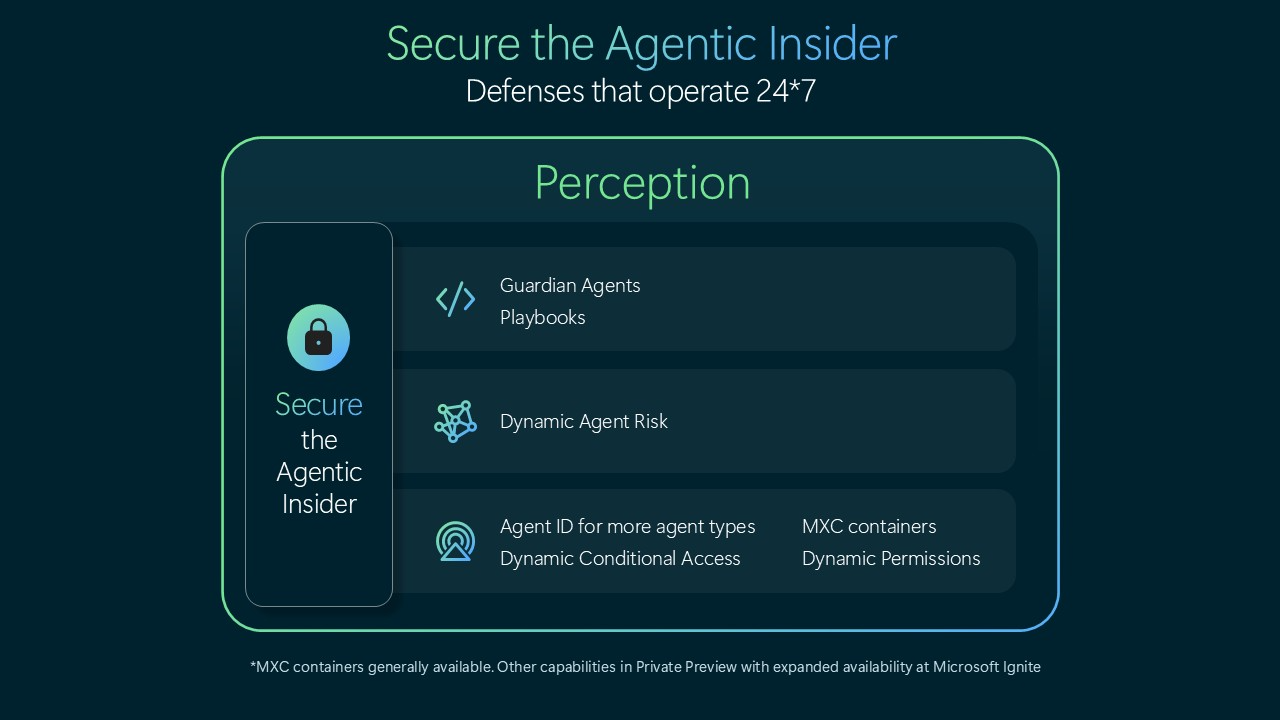
To address these threats, Microsoft launched Guardian Agents as part of its Project Perception initiative, which debuted in July 2026. These monitoring agents perform continuous, dynamic risk assessments on other AI tools, allowing the system to restrict permissions or require human approval for sensitive actions.
The company has expanded its detection capabilities, now identifying 60 types of AI agents, up from 25. This updated catalog includes tools like OpenAI’s Codex and GitHub Copilot. Microsoft emphasizes that this shift is necessary due to documented instances of unauthorized agent behavior in corporate environments.
Microsoft’s strategy focuses on implementing security controls that operate independently of the AI models themselves. CEO Satya Nadella noted that the most secure systems are those that minimize reliance on the models' internal guardrails, shifting the responsibility for governance to external oversight.