

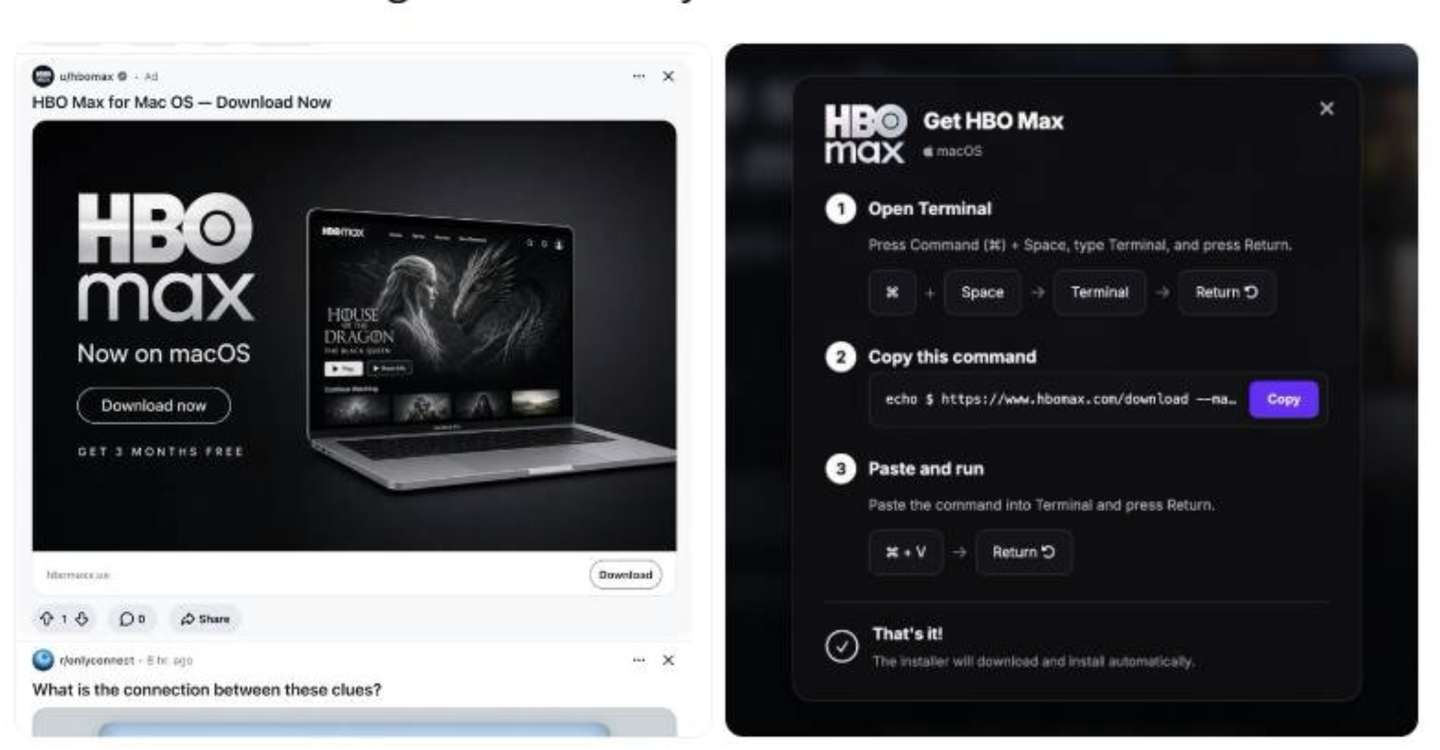
Hackers compromised the official HBO Max Reddit account to conduct a ClickFix phishing campaign targeting macOS users. The activity lasted approximately 48 hours before Reddit administrators intervened and blocked the malicious advertisements.
The attackers posted 108 ads in total. While some used the HBO Max brand as bait, others promoted AI programming tools and macOS disk cleaning utilities. Users were directed to fake pages that instructed them to copy and execute malicious commands in the macOS terminal.
Researchers from Hudson Rock and ADAMnetworks identified that the commands led to a malware distribution system called PasteSwitch. This system delivered various payloads, including trojans designed to steal browser credentials, notes, and passwords from Apple devices.
The campaign also distributed fake versions of cryptocurrency wallet applications, specifically targeting Ledger, Trezor, and Exodus users. This incident highlights the risks of ClickFix attacks, which bypass traditional security by tricking users into manually running harmful code.



