Between October 11 and 12, French supermarkets experienced a cyberattack on refrigeration systems. Attackers switched units to defrost mode, causing temperatures to rise to 50 degrees Celsius and triggering fires in some cases. Retailers including Carrefour, Les Mousquetaires, and Monoprix reported hundreds of affected stores, leading to significant food waste and potential losses in the millions of euros.
The French cybersecurity agency CERT-FR identified breaches in remote control systems from Danfoss and Copeland. Investigations focus on AK-SM and AK-SC series controllers, as well as XWEB units. Many affected devices were legacy models with known vulnerabilities. As of now, the identity of the attackers and the specific intrusion methods remain undisclosed by the Paris prosecutor's office.
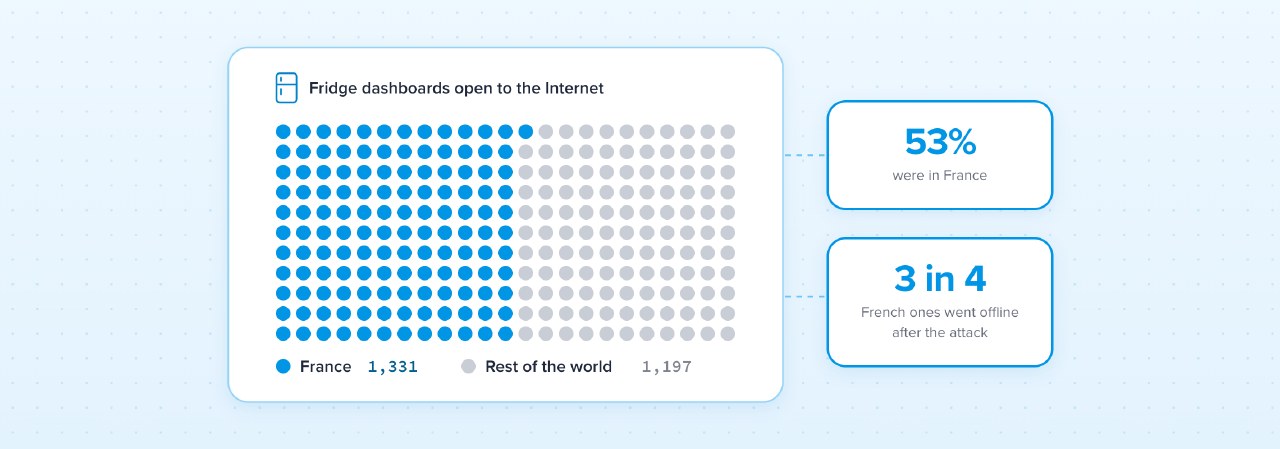
Data from IPinfo reveals that prior to the attack, 2528 Danfoss StoreView panels were accessible via the public internet globally, with 1331 located in France. Analysis shows that 85 percent of these French panels ran software with known security flaws. Many devices had been exposed for at least six months, with hundreds lacking security patches from 2023 or 2025.
Following the incident, the number of publicly accessible panels in France dropped by approximately 76 percent. IPinfo and Censys observed that many operators disconnected devices from the internet rather than applying firmware updates. CERT-FR advises operators to remove public access, utilize secure VPNs, update firmware, and change default passwords to mitigate ongoing risks.