

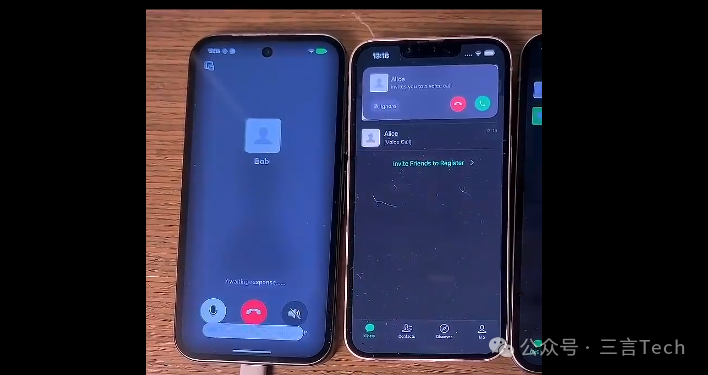
Security research firm Calif Research has disclosed a zero-click vulnerability dubbed WeWorm affecting WeChat. The exploit allows attackers to hijack a user's account simply by initiating a voice call, without requiring the victim to answer, click any links, or provide credentials. The malicious process triggers during the ringing phase, making it difficult for users to defend against.
Once compromised, the account gains the ability to automatically propagate the exploit by calling other users, functioning like a worm. The vulnerability is cross-platform, affecting both Android and iOS devices. Attackers who successfully exploit the flaw gain full control over the account, enabling them to read chat histories, send messages, and make calls under the victim's identity.
The research team identified the vulnerability in July using artificial intelligence to discover the flaw, which was subsequently confirmed by human researchers. While reports indicate that the issue has been addressed in WeChat versions Android 8.0.77 and iOS 8.0.76, the company has not provided detailed public disclosures, merely stating that they have fixed known issues.
Experts have raised concerns regarding the complexity of the application's codebase, suggesting that such zero-day vulnerabilities pose significant risks to the platform's massive user base. The use of AI in discovering this exploit highlights a growing trend in cybersecurity, where automated tools are increasingly capable of finding critical security gaps, accelerating the pace of digital attacks.


