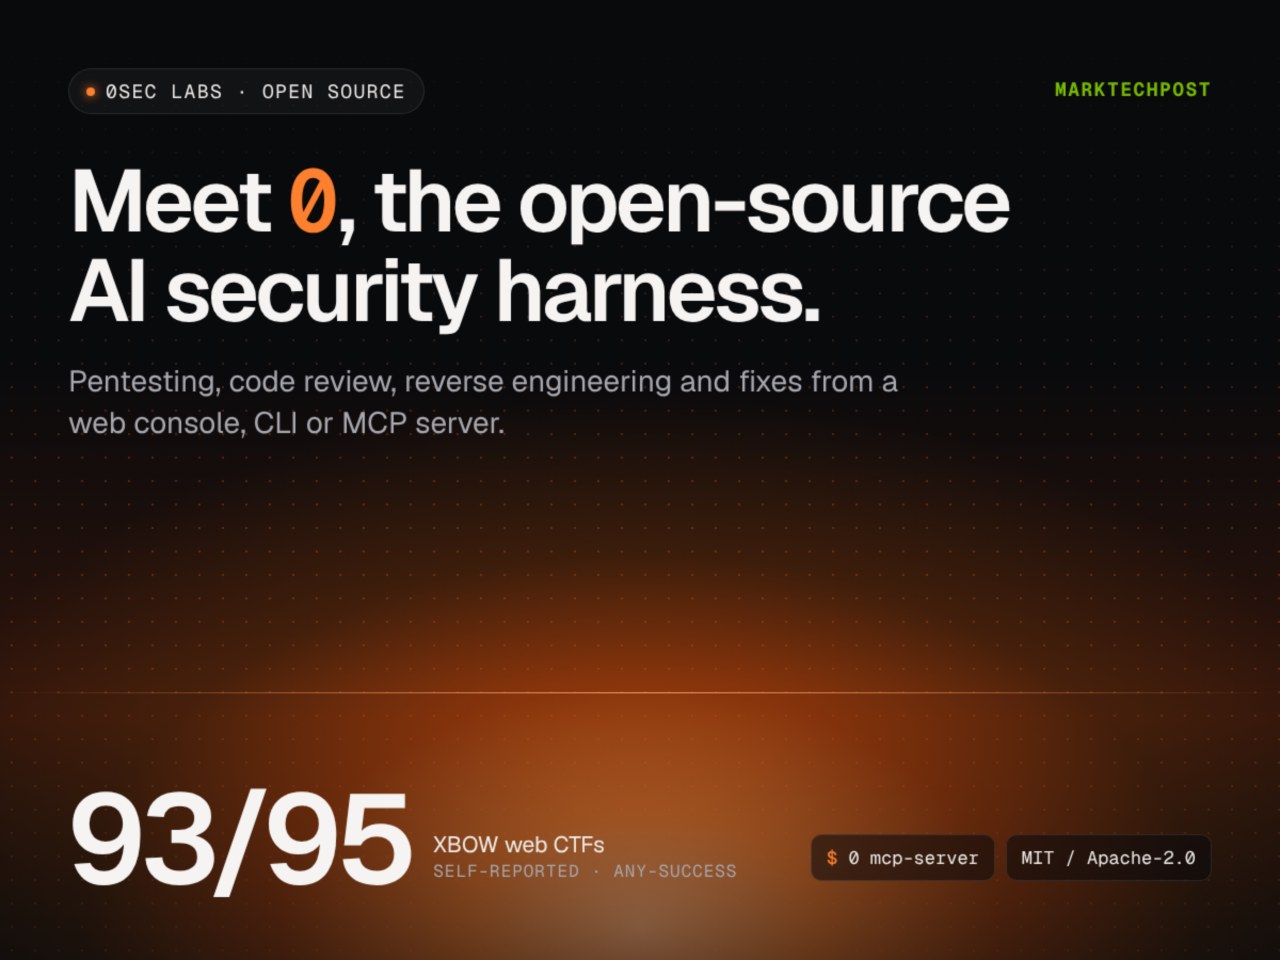
0sec Labs has released 0, an open-source control plane designed for LLM-based security workflows. The platform is not a model itself but integrates with various providers to execute security scans against authorized targets. The project is backed by Y Combinator.
The architecture utilizes a shell-first approach for web pentesting, employing tools like bash, curl, python3, and sqlmap. For compiled targets, the system uses the 0verse engine, which incorporates Ghidra, angr, and AFL++. A local MCP server provides 9 tools for scanning, triage, and reporting.
Users can access the platform via a local browser console or a CLI. The system supports multiple model providers, including OpenAI, Anthropic, DeepSeek, OpenRouter, Azure, Qwen, Kimi, GLM, and Grok. It also supports runtimes for Claude, Codex, and Gemini.
The research team reports that the tool has identified over 30 Linux kernel 0-day vulnerabilities across subsystems such as Bluetooth, NFC, and TIPC. It also covers CVEs in libraries like jsonata, node-forge, and protobuf.js.
While the open-source version is free, users are responsible for model provider costs. A hosted version, 0cloud, is currently waitlisted. The pricing structure for the hosted service includes $100 in trial credits and a fee of $5 per pull request security test.