

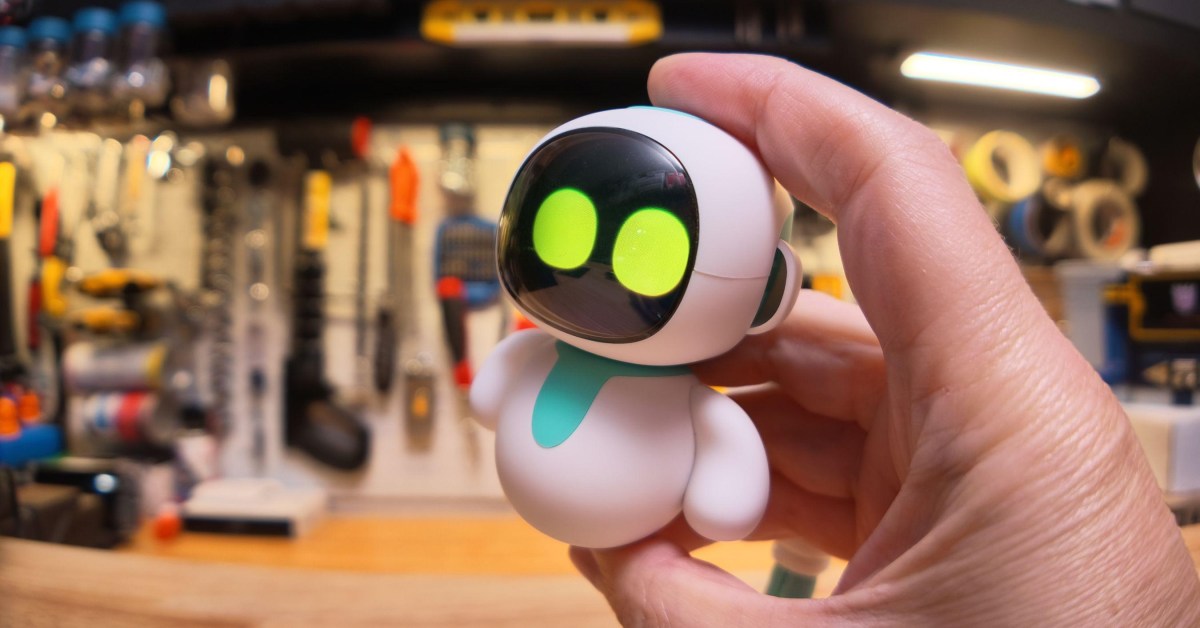
Security researcher Sammy Azdoufal discovered critical vulnerabilities in the Eiliko robot toy produced by Energize Lab. The device transmits user data to servers in China, where it remains unprotected and accessible to unauthorized parties.
The exposed database contains 13 million conversations from 68 000 active devices worldwide. Data includes user names, ages, birthdays, professions, and personal details, with over 31 000 profiles identified as belonging to children in the United States.
Energize Lab stores unencrypted photos of children and audio recordings at public web addresses, despite claims in its privacy policy that such data is deleted after processing. Researchers also found weak administrative passwords within the company's systems.
Azdoufal demonstrated that the robot's LLM can be remotely hijacked to alter its personality and responses. He is currently working with Tod Beardsley to publish nine official CVE vulnerability reports regarding these security flaws.
The manufacturer failed to respond to multiple inquiries from The Verge and the researcher over the course of a month. Attempts to contact various departments, including PR and technical support, resulted in no meaningful engagement regarding the security breach.


