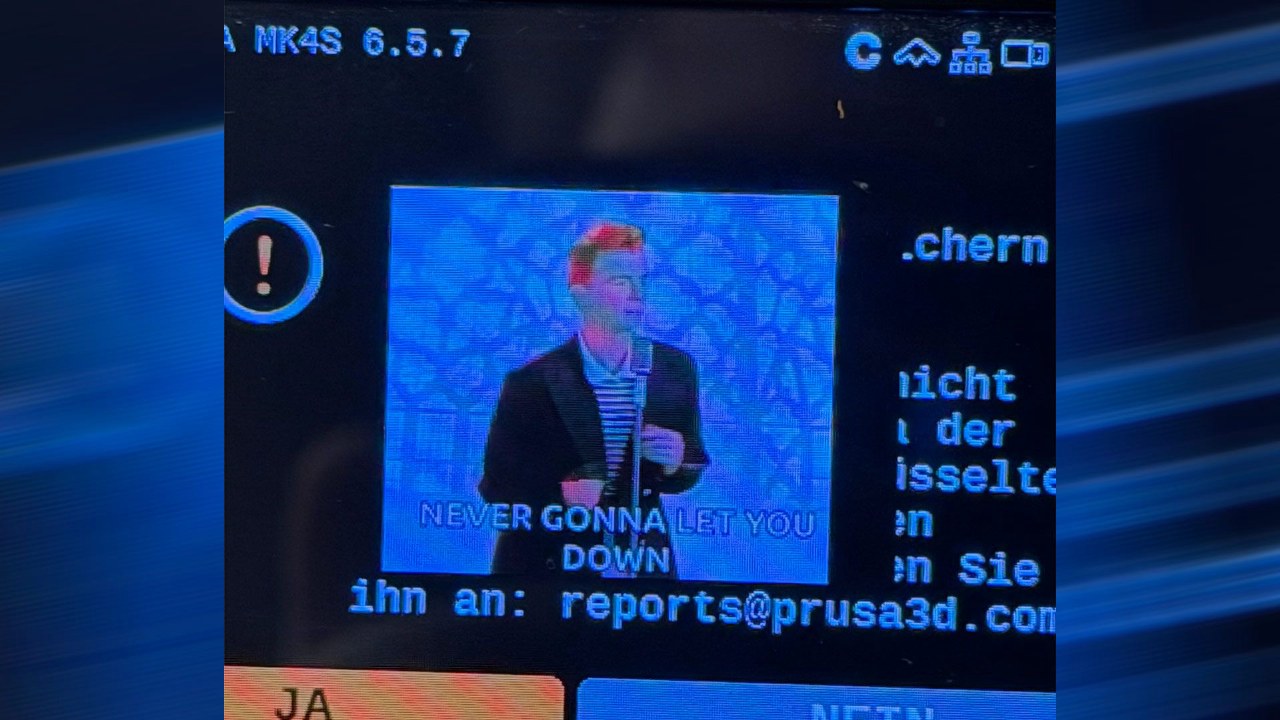
Freelance engineer Dixken spent one week testing the Prusa MK4S 3D printer for security vulnerabilities. Using Claude Opus 4.8 and a fuzzer, the researcher identified 14 findings, totaling approximately 23 individual defects within the Prusa Buddy firmware.
The most critical discovery is a remote code execution (RCE) exploit located in the Prusa Connect management platform. This vulnerability received a high severity score of 8.1. The researcher demonstrated the flaw by remotely triggering a Rickroll video on the printer's interface.
Other identified security issues include heap overflows caused by malformed encrypted print files, USB filename attacks, and network denial-of-service flaws. Many of these defects appear to stem from the use of assert statements in the original firmware development.
Following the disclosure, Prusa responded to the findings within 24 hours. The company coordinated with the researcher to address the reported vulnerabilities, marking a professional and efficient resolution to the security audit.