

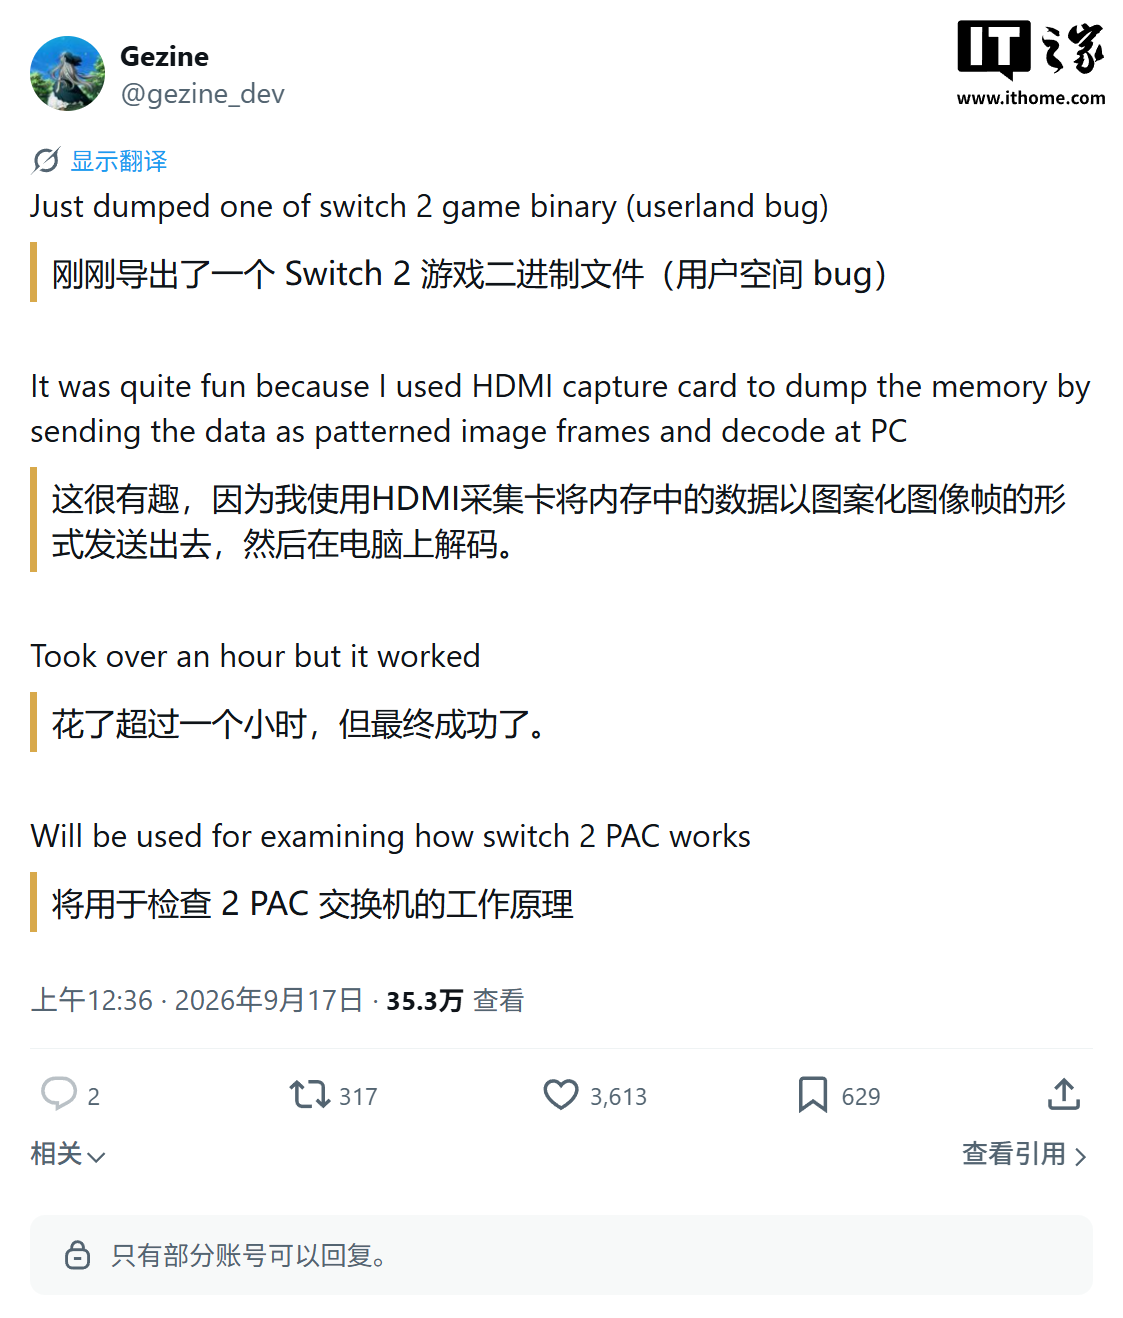
Security researcher gezine_dev announced the extraction of executable code from a Switch 2 game. The researcher utilized a userland bug within the game process to access memory data that is typically restricted from direct export.
Due to the lack of traditional debugging interfaces or file system access, the researcher mapped memory bytes into visual patterns. These patterns were displayed as pixels and color blocks on the screen, then captured via an HDMI capture card.
The captured video frames were decoded on a computer to reconstruct the original binary data. This process involved multiple cycles of display, capture, and verification to ensure the integrity of the extracted code for reverse engineering.
The researcher previously disclosed a userland exploit in July 2026 that functions on both Switch 1 and Switch 2. This exploit uses ARM64 ROP techniques to execute arbitrary code within a restricted process space.
The current findings are limited to user-level access and do not constitute a kernel exploit. The system remains protected by sandboxing and permission isolation, meaning full jailbreaking or the execution of custom firmware is not yet possible.



