

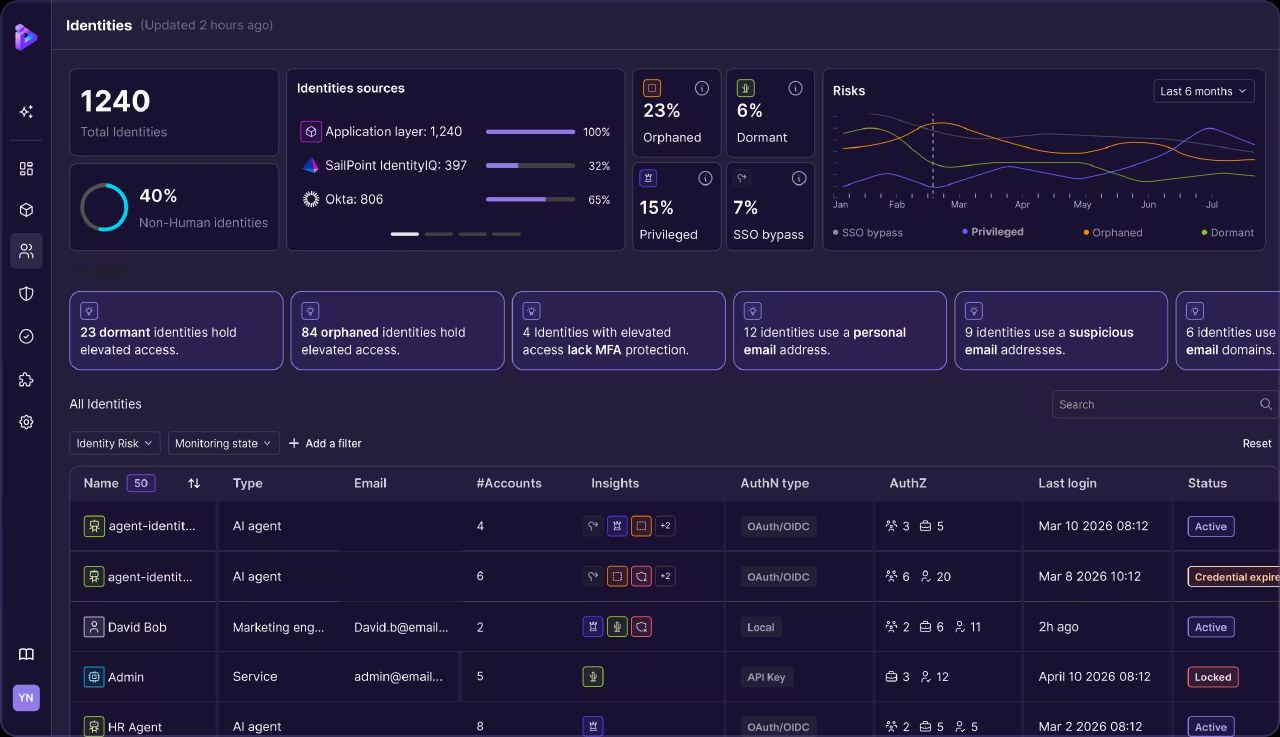
Orchid Security has introduced identity drift detection and application-level kill switches for AI agents within its Identity Control Plane. These tools allow security teams to revoke an agent's authority immediately when its behavior deviates from approved parameters.
The company's "The Identity Gap: 2026 Snapshot" report from May reveals that invisible identities outnumber visible ones 57% to 43%. Two-thirds of nonhuman accounts in the sample were provisioned inside applications, remaining hidden from identity and access management tools.
The platform now offers five key capabilities: AI readiness tagging for applications and identities, hygiene findings for orphaned or suspicious accounts, continuous drift detection, orchestrated response via existing security tools, and an audit generator for activity documentation.
Response actions range from trimming permissions and revoking credentials to disconnecting tools or suspending workflows. The application-level kill switch provides the most extreme measure by terminating the agent's operational authority.
The update includes two new integrations: a certified connector for Palo Alto Networks' Idira platform to discover and manage privileged accounts, and a telemetry stream for Splunk Enterprise Security for incident response.
Orchid Security was co-led by Team8 Capital and Intel Capital in a seed round of $36 million in January 2025. The company's governance orchestration was certified by SailPoint Technologies in September 2025.


