Security researcher Nightmare Eclipse has disclosed a zero-day vulnerability in Microsoft Defender, dubbed ShieldCrash. The flaw was identified following the release of the latest Windows 11 cumulative update.
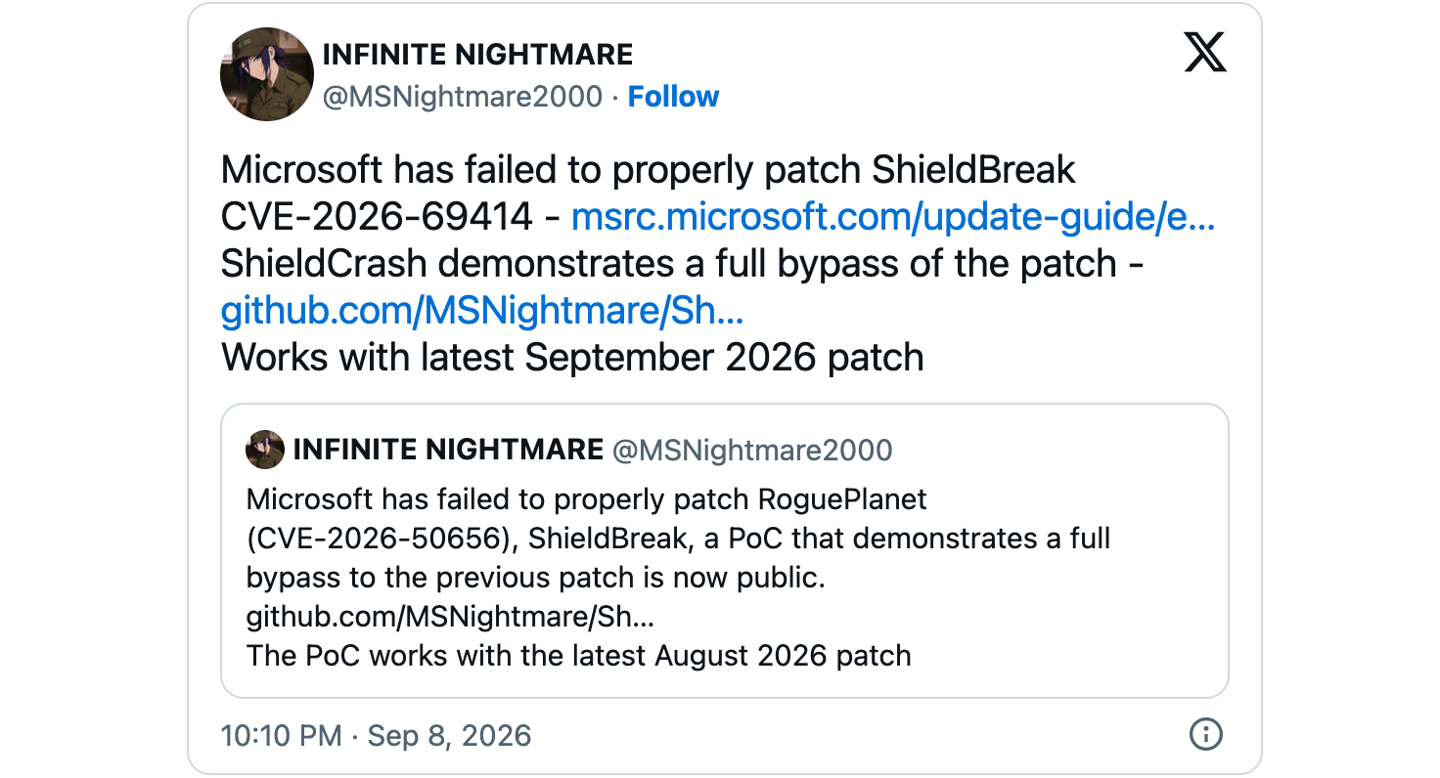
The vulnerability affects multiple versions of Windows 10, Windows 11, and Windows Server. According to the researcher, ShieldCrash is related to a previously identified issue known as ShieldBreak, which was tracked as CVE-2026-69414 and addressed in the recent update.
The researcher claims that while Microsoft patched some conditions of the original flaw, a specific trigger point remains active. Exploiting this vulnerability allows an attacker to read arbitrary system files with SYSTEM-level privileges.
The disclosure follows a series of reports from Nightmare Eclipse, who has identified multiple zero-day vulnerabilities since April 2026, including LegacyHive, RoguePlanet, and BlueHammer. The researcher remains in an ongoing dispute with Microsoft regarding vulnerability disclosure practices and bug bounty programs.
While Microsoft has released patches for several of the reported issues, including ShieldBreak, many of the other vulnerabilities identified by the researcher currently lack official fixes.