Microsoft has acknowledged that the September cumulative update KB5124008 for Windows 11 may cause domain trust relationship failures. The company is currently investigating the reports and plans to provide updates as more information becomes available.
System administrators reported that Windows 11 25H2 workstations experienced login failures after installing the update. In one instance, 11 out of 256 enterprise devices lost domain trust, leading to widespread Kerberos authentication errors and a fallback to NTLM and Netlogon protocols.
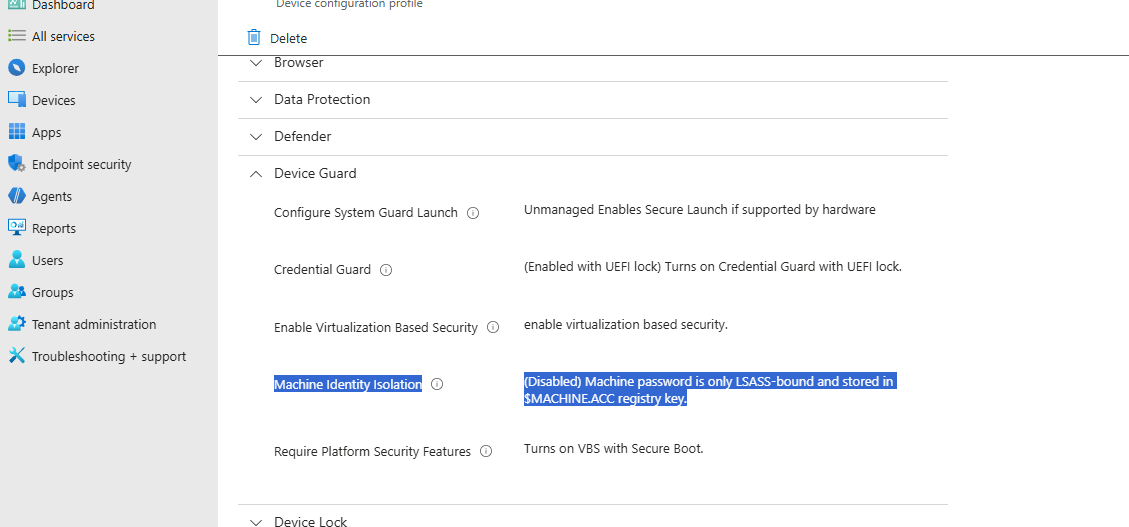
The issue appears linked to the Machine Identity Isolation setting, which is part of Virtualization-Based Security and Credential Guard. After the update, the registry value for MachineIdentityIsolation is set to 2, forcing the system to move computer account keys into Credential Guard and remove copies from the Local Security Authority.
To resolve the issue, some administrators have manually changed the registry value at HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\Control\Lsa back to 0. Following this change and a system reboot, they used PowerShell to repair the secure channel, which restored device access.