

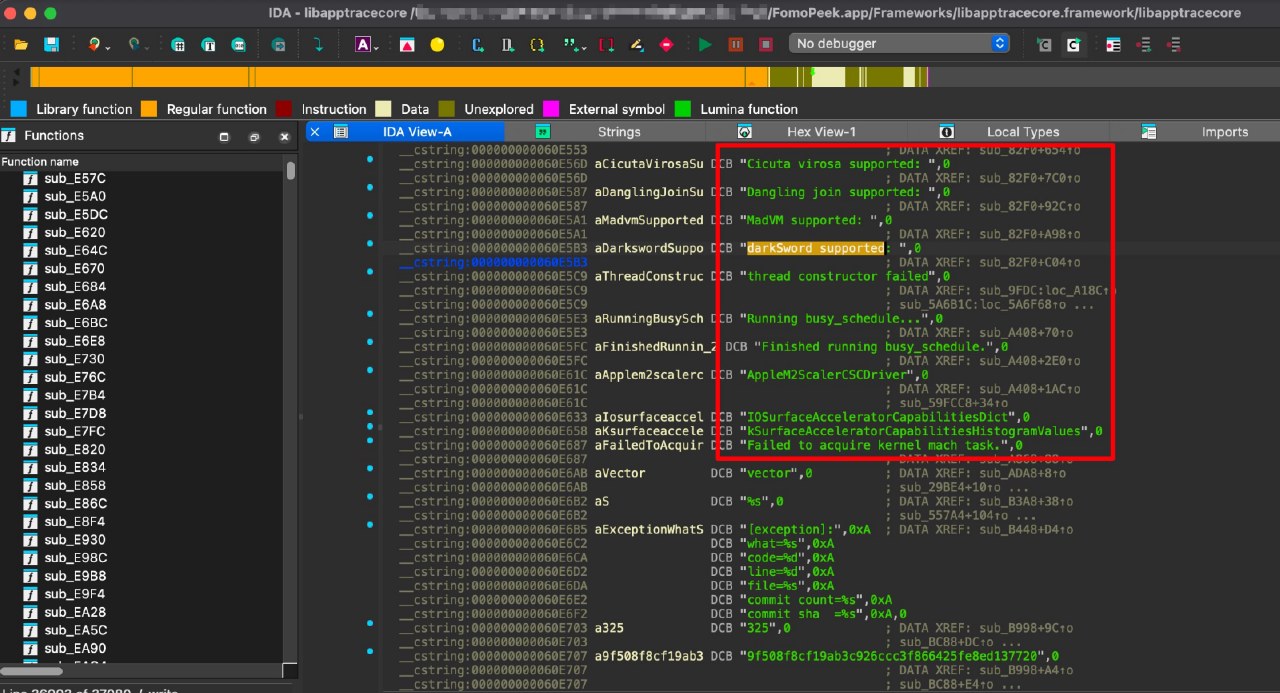
Security firm SlowMist reported that the FomoPeek application has been stealing private keys from users. Although marketed as a tool for tracking on-chain fund movements, the app contains hidden modules that exploit iOS kernel-level vulnerabilities to bypass sandbox protections and access sensitive data.
The malicious framework within FomoPeek can decrypt keychain data, including cryptocurrency private keys, seed phrases, and login credentials. It is capable of reading files from other applications and receiving remote commands from attacker-controlled servers to exfiltrate information.
The exploit targets vulnerabilities in iOS versions 12.0 through 18.7 and 26.0 through 26.1. These are known issues previously disclosed by Google in March 2026 as part of the DarkSword series. Apple has already released patches for these security flaws in newer updates.
To attract users, FomoPeek utilized influencer marketing, offering a reward of $7 in USDT to new users who signed up using referral codes. This strategy allowed the developers to quickly reach a large number of cryptocurrency users and drain their wallets.
Experts emphasize that users should keep their devices updated to the latest iOS version to mitigate these risks. Similar attack frameworks have been observed in other malicious campaigns, such as fake VPS service promotions, highlighting the need to avoid untrusted software.



