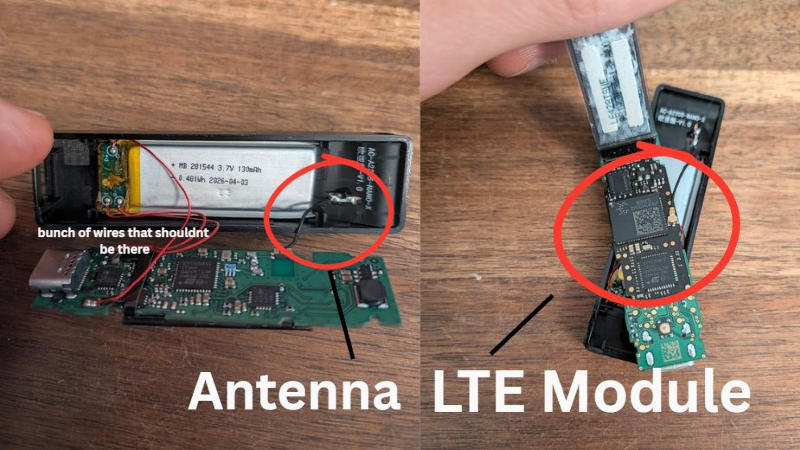
Compromised Ledger hardware wallets have been identified, leading to the theft of over $93 million in assets. These devices were modified by third-party resellers to include eSIM and LTE modules, which capture seed phrases during the initial setup process via a flexible circuit board installed under the display.
The issue primarily affects units purchased through unauthorized resellers, such as Cryptobilis, which has ceased operations. Reports indicate that compromised devices were also found at MediaMarkt retail locations, with at least one unit traced back to the European distributor Aqipa GmbH. Investigations suggest the modifications are now being produced on an industrial scale.
Ledger confirmed that devices purchased directly from the company are not affected. The manufacturer advises users who bought wallets from Cryptobilis in the last 90 days not to perform the initial setup. Those who have already configured their devices are urged to transfer funds to a new wallet immediately.
To mitigate risks, Ledger has released visual guides for verifying the physical integrity of their hardware. Users are also strongly advised to download software exclusively from the official company website to avoid malicious versions distributed by fraudulent platforms.