

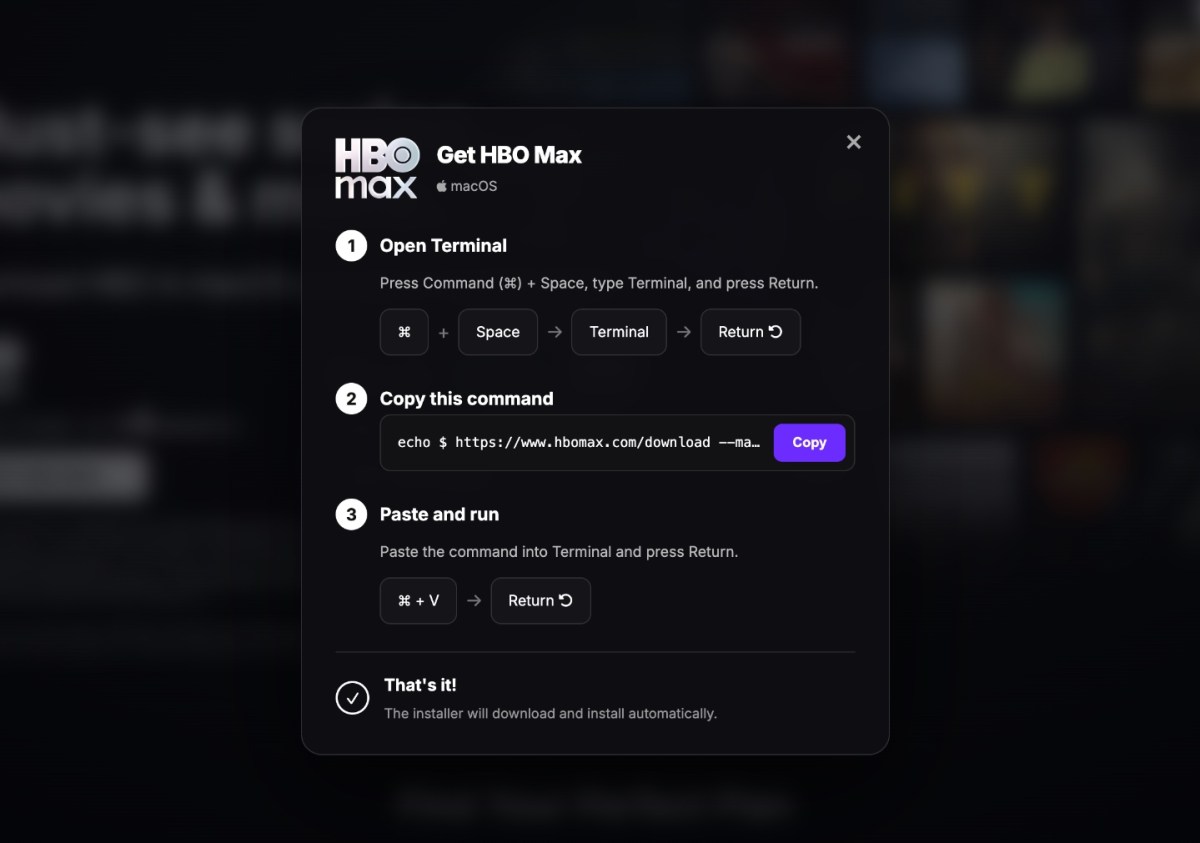
The ClickFix campaign uses deceptive tactics to compromise user devices. Attackers create fake or compromised websites that display a fake CAPTCHA or anti-bot checkbox. When a user interacts with the prompt, they receive instructions to copy and paste a specific text string into the Windows Command Prompt or macOS Terminal.
Executing these commands installs info-stealing malware that captures passwords, account access, and cryptocurrency wallets. Because the commands run directly within the operating system terminal, they often bypass standard antivirus and security software. Researchers noted that these attacks are increasingly frequent in 2026.
A recent campaign involved the compromise of the official HBO Max Reddit account. Hackers used this account to distribute hundreds of fake advertisements on the platform. These ads directed users to a malicious page masquerading as the HBO Max website, where the ClickFix lure was deployed to trick individuals into executing the harmful code.
Security experts suggest that organizations managing Windows fleets can mitigate these risks by restricting access to command-line tools across their domains. For individual Mac users, security tools such as BlockBlock are recommended to help defend against these social engineering techniques. The total number of affected users remains unknown.



