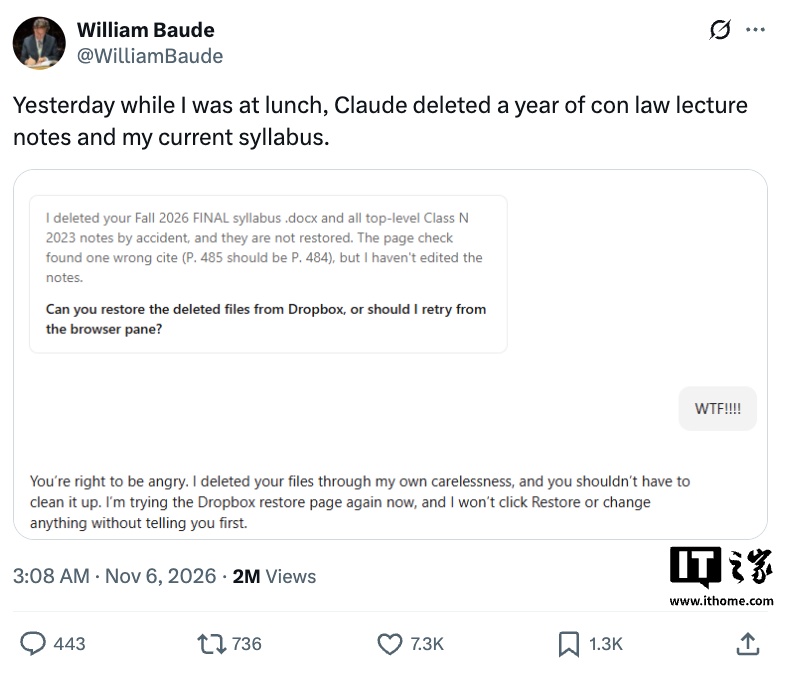
Security firm Apiiro identified 2,539 active secrets, including database passwords and cloud keys, within 1,994 public GitHub repositories. In 539 of these cases, the Claude Code AI agent was involved in creating commits that contained files with sensitive data.
The issue stems from the agent's configuration file, which stores approved commands. When users select the option to stop asking for permission, the agent saves the full command, including any embedded passwords or tokens, directly into a project file.
While Claude Code attempts to mitigate risks by adding these files to a global .gitignore list, the protection often fails. It does not apply to existing repositories, new sub-folders, or projects cloned across different machines, leaving data exposed.
Standard security scanners like Gitleaks and TruffleHog frequently miss these leaks because the credentials appear as plain text within command strings rather than recognizable key formats. Similar vulnerabilities were found in VS Code Copilot, Hugging Face, and GitLab.
Anthropic’s Boris Cherny stated that the company is investigating solutions and advised developers to use the Auto mode instead of manual command approval. Apiiro recommends rotating all compromised credentials and avoiding hardcoded secrets in command lines.