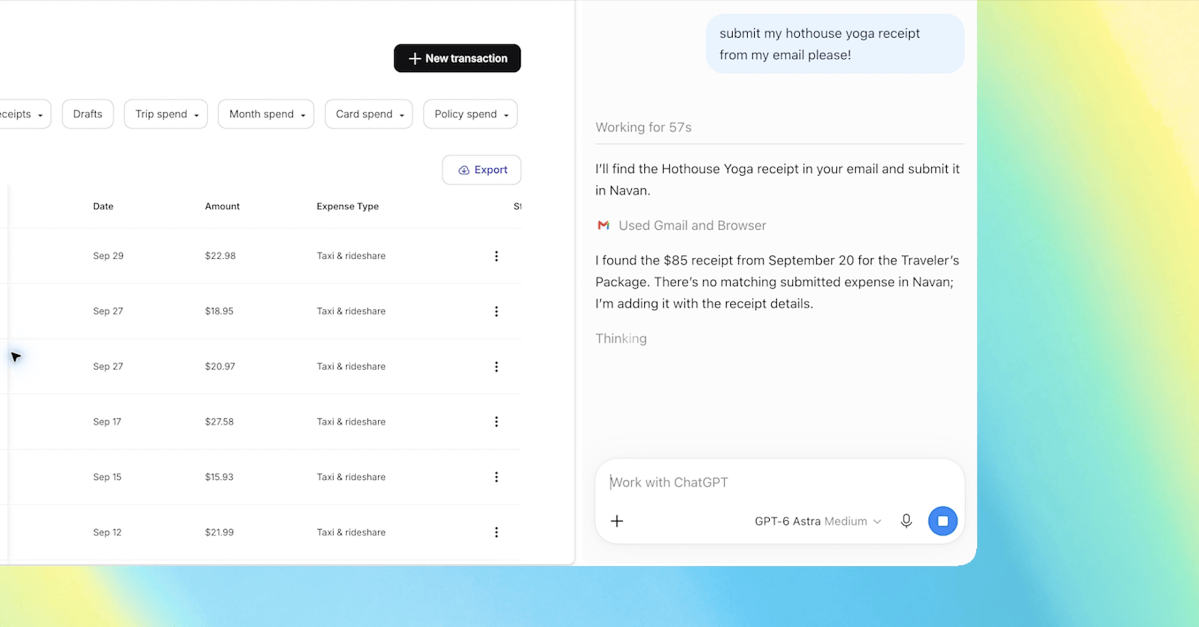
Researchers at Check Point Research identified a security vulnerability in the integration between ChatGPT and Gmail. The flaw allowed for the linking of independent accounts, enabling data transfer between them through a shared internal JFrog Artifactory instance used for loading dependencies.
The mechanism, dubbed a shared clipboard, allowed containers to write data to object properties and read them from another account. In a demonstration, an attacker could send a hidden task to a victim's session, causing the AI to read connected Gmail data and transmit the results to an external account.
The vulnerability was discovered in June 2026 and publicly disclosed on September 8, 2026. OpenAI confirmed that the affected Artifactory instance has since been decommissioned, and the channel is no longer accessible as of September 10, 2026.
The potential impact of the exploit depended on the permissions granted to the AI session, including access to email history, files, and other integrated applications. Users were at risk if they opened compromised shared chats, used malicious prompts, or interacted with custom GPTs.