Security researchers from Proofpoint and Volexity have identified a campaign using the BlueMoon exploit kit. The attacks target Windows 10 and Windows 11 users to execute remote code and steal sensitive information.
The campaign involves groups such as JungleBamboo, also known as APT31 or Violet Typhoon, and UTA0560. These actors have been active since late August, focusing their efforts on corporate entities and non-governmental organizations.
The exploit chain leverages three specific vulnerabilities: CVE-2026-85046 in the Chrome V8 engine, the sandbox escape flaw CVE-2026-87491, and the Windows ALPC heap buffer overflow CVE-2026-85880 for privilege escalation.
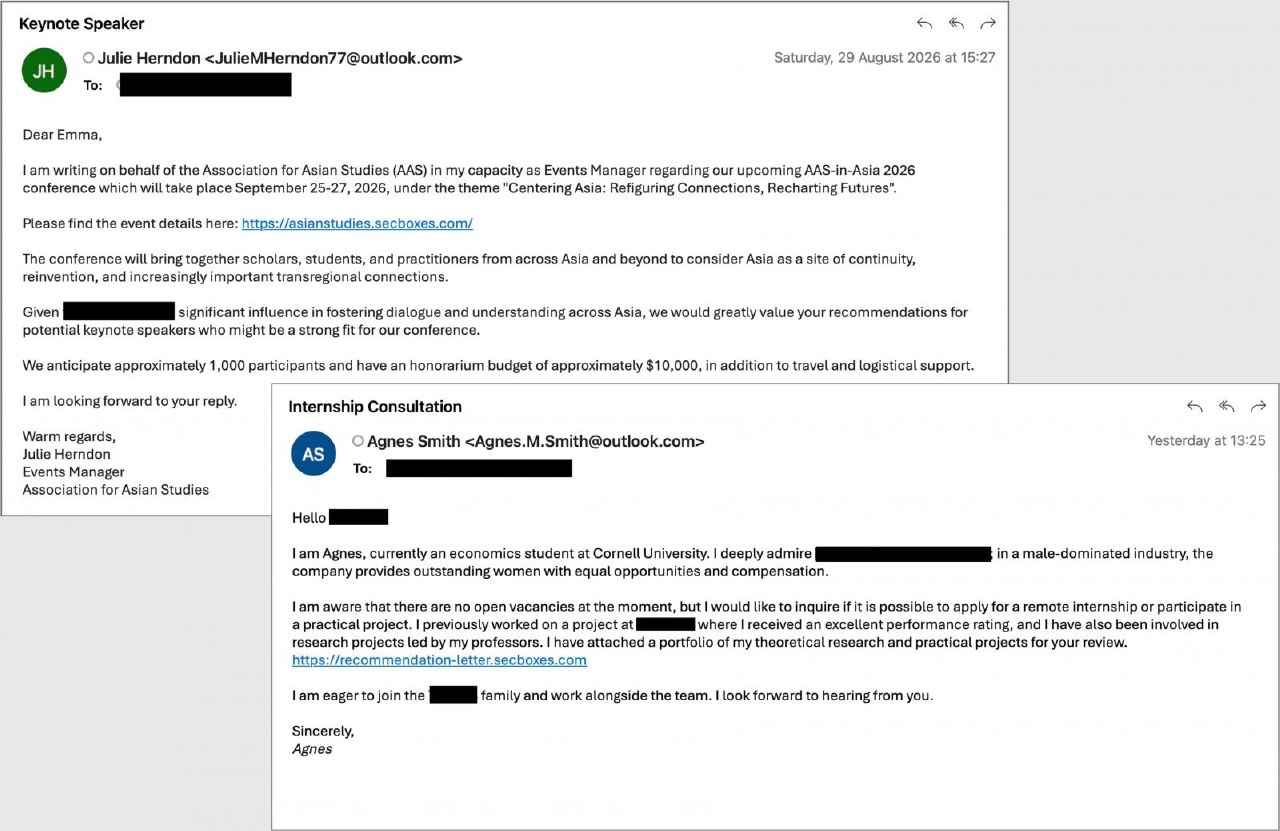
Attackers distribute the malware via emails disguised as donation requests, business proposals, or meeting invitations. Once a user is compromised, the kit attempts to run exploits within a Web Worker, with a maximum of five retry attempts.
The process involves identifying the target device, escalating privileges to inject code into the Chrome parent process, and downloading malicious loaders via curl. Attackers exploit the time gap between Chromium public fixes and stable releases.