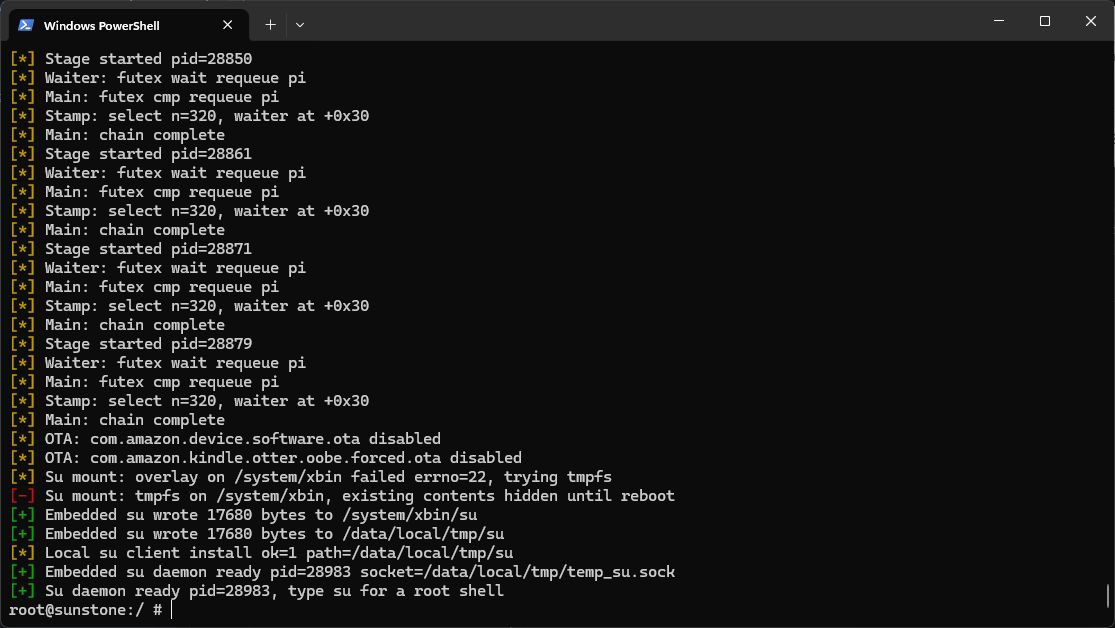
For users of the Amazon Fire Max 11 (2023), a new method has emerged to gain more control over the device. A member of the xda-developers community, Rortiz2, published instructions on how to spawn a temporary root shell for quick access, allowing for system-level changes that are not officially supported by Amazon.
The exploit leverages a security vulnerability in Fire OS 8.3 with a Linux 5.10 kernel. By connecting the tablet to a PC and using a command-line tool, users can open a root shell prompt. This allows them to disable the stock Amazon launcher, provided a third-party launcher is installed first to avoid losing access to the home screen.
The exploit also automatically disables over-the-air updates to prevent security patches from fixing the vulnerability or restoring the default launcher. While users can manually re-enable updates, the author notes that the tablet itself is not fully rooted through this specific exploit, meaning apps requiring root access will not work.
Recent updates to the method have expanded its capabilities. It is now possible to unlock the bootloader, obtain permanent root access, install a custom recovery, and upgrade or downgrade FireOS. Theoretically, this also allows for the loading of custom ROMs to replace the Fire OS interface.