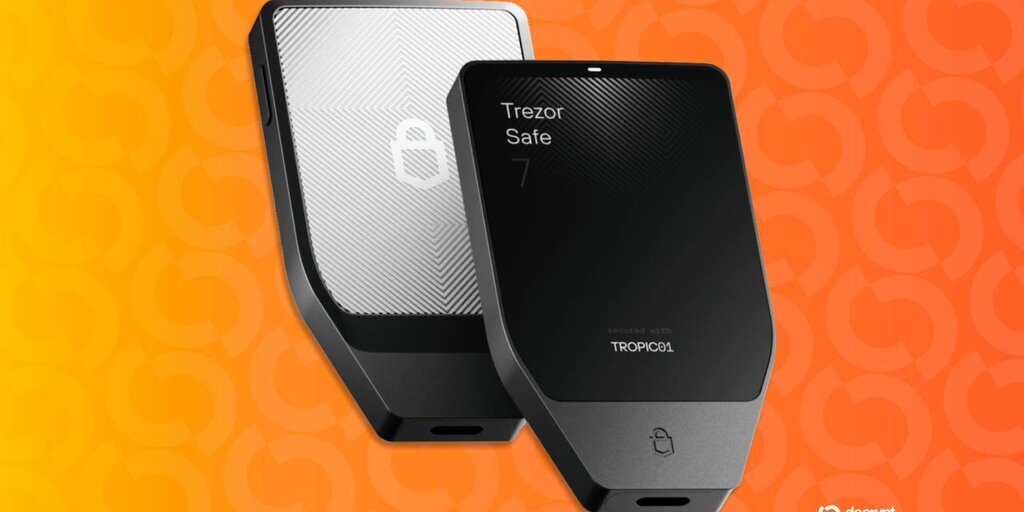
Trezor is terminating its authorized reseller network, with all current partner agreements set to expire on January 1, 2027. The company stated this move is a precautionary measure to strengthen supply chain security and improve oversight of its distribution partners.
The decision follows a security investigation by Ledger, which discovered a malicious spy implant in hardware wallets sold by the third-party retailer CryptoBilis. The unauthorized component was designed to capture recovery phrases and transmit them via an embedded eSIM over LTE networks.
While Trezor emphasized that there is no evidence of compromised Trezor devices, the company will stop supplying new stock to affected resellers. Current partners may continue selling existing inventory through the upcoming holiday season.
Trezor plans to implement stricter rules and an updated legal framework for the remaining authorized sellers. The company previously reported a data breach involving 80,689 customers in September following unauthorized access at its shipping partner, ShipMonk.