Kubernetes remains the second most popular open-source project globally, trailing only Linux. In Russia, over 53% of companies utilize vanilla Kubernetes, excluding those relying on commercial or managed cloud services. Despite the existence of more than 100 specialized security tools and numerous best practices, organizations continue to face significant challenges in securing their containerized environments.
According to the Red Hat State of Kubernetes Security 2024 report, 46% of companies incurred financial losses due to inadequate Kubernetes security measures. Furthermore, 9 out of 10 organizations reported at least one security incident related to their containers or Kubernetes clusters. These statistics highlight a persistent gap between available security tooling and actual operational safety.
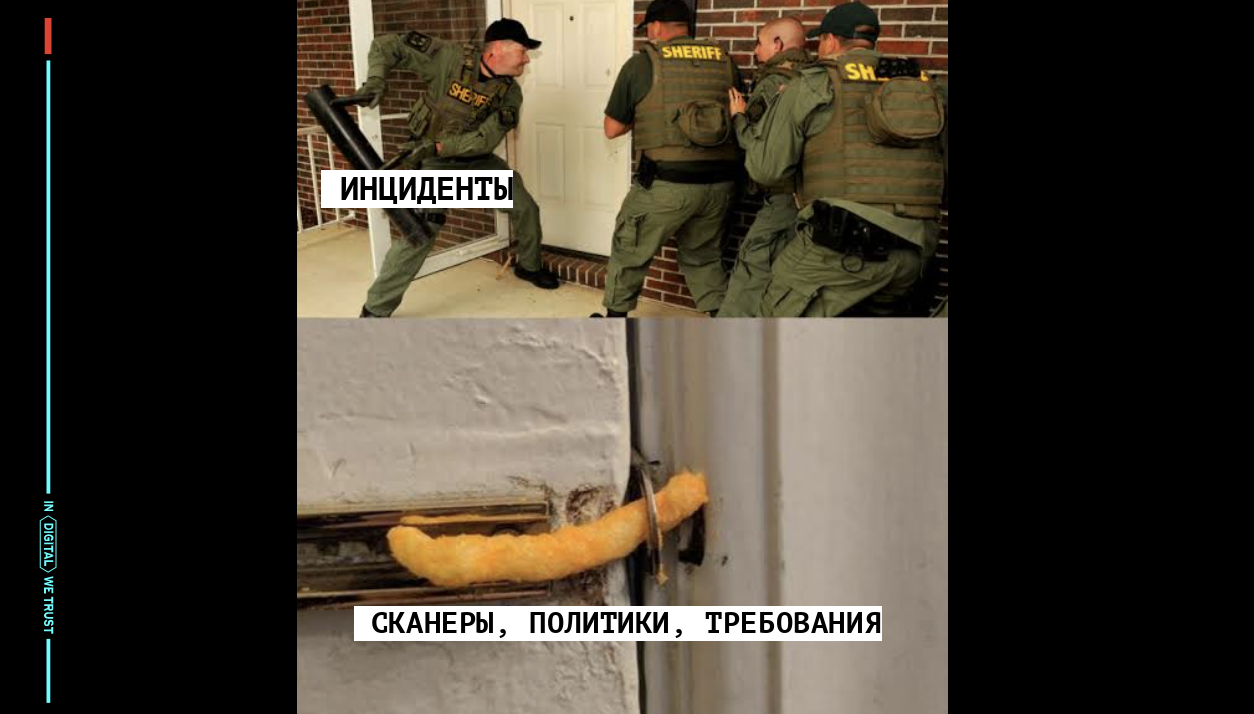
Experts emphasize that deploying scanners or implementing policies does not guarantee protection. Security requires a systemic approach rather than reliance on individual tools. The focus should be on building security as a core business function, particularly when managing environments that scale to hundreds of clusters, requiring clearly defined team responsibilities and robust internal processes.