Nintendo has issued a security advisory regarding a critical vulnerability found in older firmware versions of the Switch console. The flaw, identified as CVE-2026-82079, allows for remote code execution, which could potentially lead to unauthorized data access.
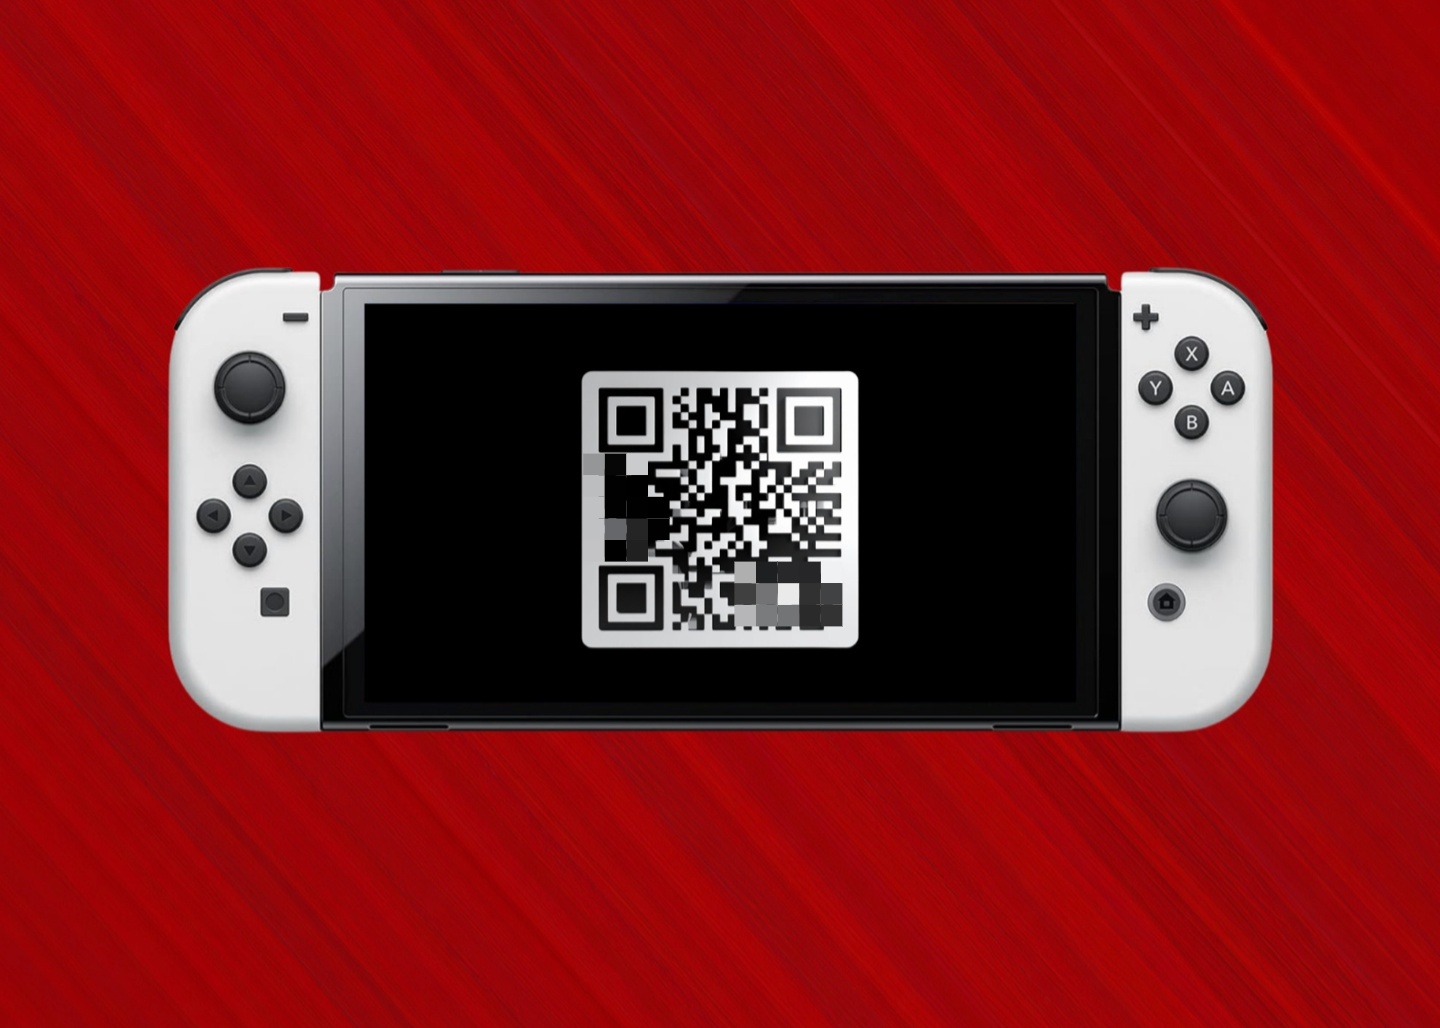
The vulnerability is linked to the QR code pairing mechanism used within the console's Album feature and the game Mario Kart Live: Home Circuit. Attackers could exploit this process when users display QR codes on the screen to transfer screenshots or video content to their smartphones.
To address the issue, Nintendo has released system update version 23.0.0. The company strongly recommends that all users install this update immediately to secure their devices against potential unauthorized code execution.
While the company notes that the risk is limited for most users due to the requirement for close-range interaction, it provides specific guidance for those unable to connect to the internet. Users are advised to avoid sharing media content in the presence of strangers.