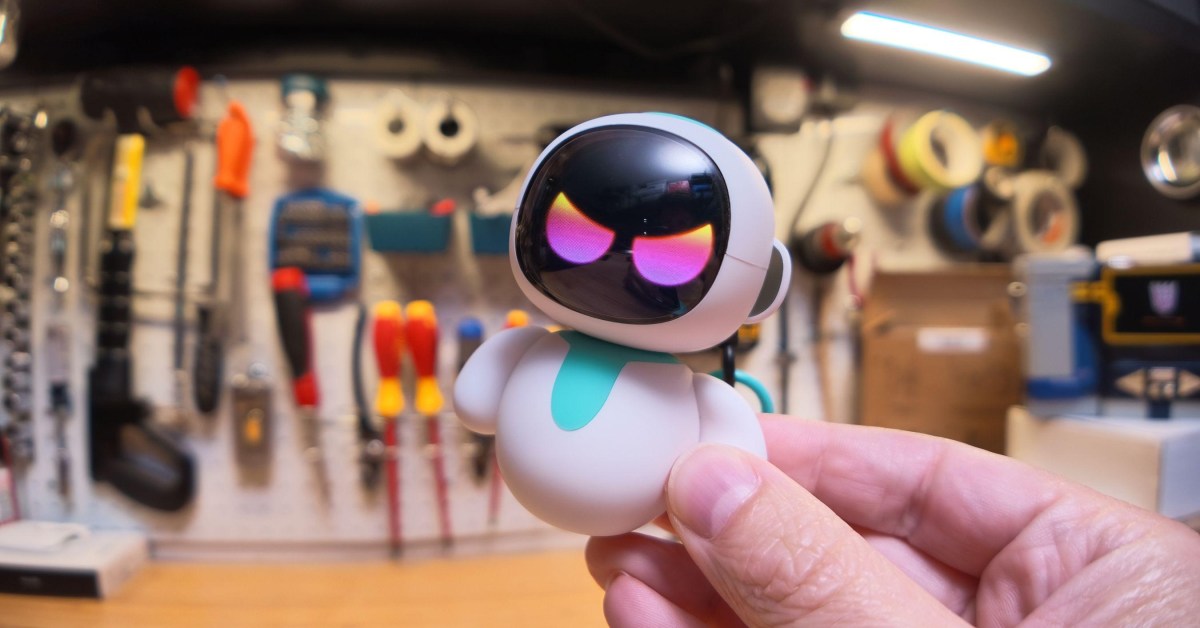
Energize Lab, the manufacturer of the Eiliko robot, has announced plans to hire an independent security firm to audit its systems. This decision follows a report by The Verge and security researcher Sammy Azdoufal, which highlighted significant vulnerabilities in the device, including unauthorized access to conversation transcripts and user data.
The company stated that it has disabled remote modification of robot responses and restricted external access to its backend systems. Additionally, Energize Lab claims it will delete existing conversation logs, user profiles, and avatar images. The firm has also established a dedicated email address, security@energizelab.com, to handle security-related inquiries.
Despite these measures, security researcher Sammy Azdoufal reports that the systems remain vulnerable. He confirmed that audio recordings and photos of users are still accessible at unsecured public web addresses. Furthermore, he retains SSH access to the robots, allowing him to read transcripts and modify device behavior, contradicting the company's claims of having secured its infrastructure.