Researchers successfully bypassed the Secure Debug protection on the Raspberry Pi RP2350 microcontroller, revision A4. The attack involved using laser fault injection to manipulate the DEBUGEN register, which controls access to the chip's memory ports.
The team utilized photon emission microscopy to pinpoint the exact physical location of the DEBUGEN register bits on the silicon die. By cycling these bits and capturing infrared emissions, they narrowed the target area to a few micrometers.
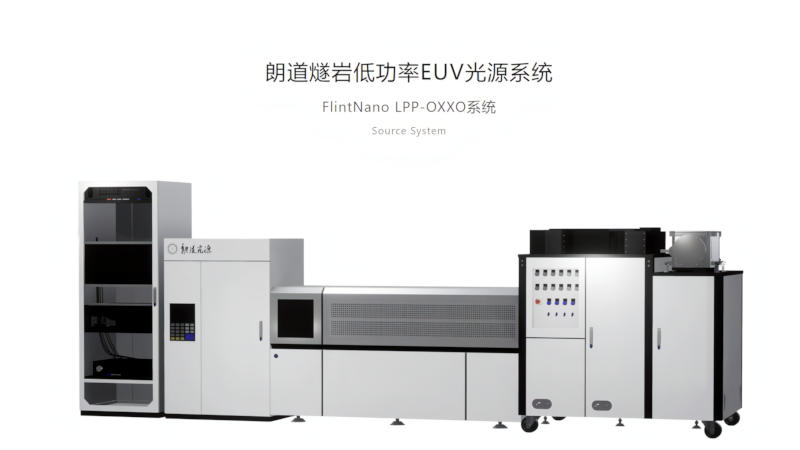
The exploit required physical access to the chip, including decapsulation of the package and soldering it to a custom test platform. The equipment used for this laboratory-grade attack is valued at approximately $250 000.
During the attack, a 980 nm pulsed laser with a power of about 1.2 W and a pulse duration of 100 ns was used to flip the target bits. This allowed the researchers to bypass the permanent debug disable flag and gain read/write access to protected memory.